So two weeks later and we’re all done. I made a couple of posts bellow about some of the trouble I had with systemd and getting everything to come back up correctly on reboot. But that’s all worked out now. I finished the scripts last night and tested everything. There was a lot of trial and error involved and I’m not really convinced that the script to lock the disks is very reliable. It seems that if anything goes wrong during the lock process it will just not lock the disks. There doesn’t appear to be an option to force a volume to lock even if it’s busy. So I’m thinking that if I want to guarantee that the disks are locked I should just shutdown the servers.
However I’ve been testing the scripts and with a fair bit of tweaking have got it working to the point where it will consistently close the disks. I’m sure I will be tweaking them some more as time goes on, but for now I’m ready to call it completed.
So much encryption
I’m going to post sections from my /etc/fstab and /etc/crypttab files so you can see how I’ve configured the disks to open and mount on startup, and also just how many disks I had to encrypt. I’ll also post the output of df -h
HELIOS
/etc/crypttab
# <target name> <source device> <key file> <options>
cryptswap1 /dev/sdi5 /dev/urandom swap,offset=1024,cipher=aes-xts-plain64
downloads /dev/disk/by-uuid/f319669a-757b-4ad2-a2c3-f83dd8f974ac /home/kane/keys/helios.downloads.key luks
data1 /dev/disk/by-uuid/853e9bdf-bf4a-481e-b873-ba6cd39d7011 /home/kane/keys/helios.data1.key luks
data2 /dev/disk/by-uuid/4b2250bd-d606-4530-babd-e9494362bfd1 /home/kane/keys/helios.data2.key luks
data3 /dev/disk/by-uuid/2811cd52-d9b2-4152-a3af-ee99fd289e23 /home/kane/keys/helios.data3.key luks
data4 /dev/disk/by-uuid/69cfb5e5-96c8-449d-b2c8-7ffe852c5525 /home/kane/keys/helios.data4.key luks
data5 /dev/disk/by-uuid/52777fbb-553f-46cd-adbb-4c96c9833ec6 /home/kane/keys/helios.data5.key luks
data6 /dev/disk/by-uuid/89b5e5e8-4bcf-42f1-becd-1d72ab05edc7 /home/kane/keys/helios.data6.key luks
data7 /dev/disk/by-uuid/ae123774-9f7c-49e8-80a1-2d8d4dd2ed9f /home/kane/keys/helios.data7.key luks
data8 /dev/disk/by-uuid/f2795c35-f1a8-490e-ad46-45ef23f319d4 /home/kane/keys/helios.data8.key luks
parity1 /dev/disk/by-uuid/05e98e23-f0cb-424c-ab12-4527321469e1 /home/kane/keys/helios.parity1.key luks
parity2 /dev/disk/by-uuid/bcd3c710-19a9-4054-aa3b-c943a59acc7a /home/kane/keys/helios.parity2.key luks
backups1 /dev/disk/by-uuid/209e9133-67fa-4023-8bfa-fc1ce11ac4e3 /home/kane/keys/helios.backups1.key luks
backups2 /dev/disk/by-uuid/197ec56d-af4b-4b66-88e3-dcdfa258c4ab /home/kane/keys/helios.backups2.key luks
/etc/fstab
# <file system> <mount point> <type> <options> <dump> <pass>
# / was on /dev/sdh1 during installation
UUID=3b7ea4d8-c728-459e-adb2-86a0abaa0324 / ext4 errors=remount-ro,noatime,discard 0 1
/dev/mapper/cryptswap1 none swap sw 0 0
tmpfs /tmp tmpfs defaults,noatime,nosuid,noexec,nodev,mode=1777,size=512M 0 0
/dev/mapper/downloads /mnt/Downloads ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
#Mount samba shares
//vps/backup /home/kane/.backup-vps cifs credentials=/home/kane/.vps-cifs,uid=1000,noauto,users 0 0
//vps/keys /home/kane/keys cifs credentials=/home/kane/.vps-cifs,auto 0 0
#Mount NFS Shares
10.10.1.220:/mnt/data1 /mnt/hyron/data1 nfs defaults 0 0
10.10.1.220:/mnt/data2 /mnt/hyron/data2 nfs defaults 0 0
#Encrypted Volumes
UUID=eeb06b1d-4009-4442-a5e5-7531ca3196ad /mnt/backups btrfs defaults,nobootwait,nofail,compress=lzo,x-systemd.requires=network.target 0 2
/dev/mapper/data1 /mnt/data1 ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
/dev/mapper/data2 /mnt/data2 ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
/dev/mapper/data3 /mnt/data3 ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
/dev/mapper/data4 /mnt/data4 ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
/dev/mapper/data5 /mnt/data5 ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
/dev/mapper/data6 /mnt/data6 ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
/dev/mapper/data7 /mnt/data7 ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
/dev/mapper/data8 /mnt/data8 ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
/dev/mapper/parity1 /mnt/parity1 ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
/dev/mapper/parity2 /mnt/parity2 ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
df -h
Filesystem Size Used Avail Use% Mounted on
udev 7.8G 0 7.8G 0% /dev
tmpfs 1.6G 35M 1.6G 3% /run
/dev/sdi1 95G 28G 62G 31% /
tmpfs 7.9G 80K 7.9G 1% /dev/shm
tmpfs 5.0M 4.0K 5.0M 1% /run/lock
tmpfs 7.9G 0 7.9G 0% /sys/fs/cgroup
tmpfs 512M 188K 512M 1% /tmp
tmpfs 1.6G 20K 1.6G 1% /run/user/108
tmpfs 1.6G 0 1.6G 0% /run/user/1000
//vps/keys 8.0G 4.7G 3.4G 59% /home/kane/keys
/dev/mapper/downloads 917G 294G 577G 34% /mnt/Downloads
/dev/mapper/data2 1.8T 1.6T 179G 90% /mnt/data2
/dev/mapper/data8 1.8T 1.6T 177G 90% /mnt/data8
/dev/mapper/parity2 1.8T 1.7T 69G 97% /mnt/parity2
/dev/mapper/backups1 1.9T 583G 1.3T 32% /mnt/backups
10.10.1.220:/mnt/data1 3.6T 2.0T 1.5T 57% /mnt/hyron/data1
10.10.1.220:/mnt/data2 3.6T 2.0T 1.5T 57% /mnt/hyron/data2
/dev/mapper/data1 1.8T 1.6T 178G 90% /mnt/data1
/dev/mapper/data3 1.8T 1.6T 194G 89% /mnt/data3
/dev/mapper/data4 1.8T 1.6T 182G 90% /mnt/data4
/dev/mapper/data5 1.8T 1.6T 183G 90% /mnt/data5
/dev/mapper/data6 1.8T 1.6T 182G 90% /mnt/data6
/dev/mapper/data7 1.8T 1.6T 190G 90% /mnt/data7
/dev/mapper/parity1 1.8T 1.7T 32G 99% /mnt/parity1
none 22T 17T 4.4T 79% /mnt/pool
HYRON
/etc/crypttab
# <target name> <source device> <key file> <options>
cryptswap1 /dev/dm-1 /dev/urandom swap,offset=1024,cipher=aes-xts-plain64
data1 /dev/disk/by-uuid/35fc9cd0-0d43-4df0-949e-c545cee47000 /home/kane/keys/hyron.data1.key luks
data2 /dev/disk/by-uuid/73f62539-a829-4166-8267-644c095ef27f /home/kane/keys/hyron.data2.key luks
parity1 /dev/disk/by-uuid/21295307-169a-4395-aa3e-821e017c5c22 /home/kane/keys/hyron.parity1.key luks
parity2 /dev/disk/by-uuid/f1e50579-212a-4774-9ba1-159b87f8e4b0 /home/kane/keys/hyron.parity2.key luks
/etc/fstab
# <file system> <mount point> <type> <options> <dump> <pass>
/dev/mapper/hyron--vg-root / ext4 errors=remount-ro,noatime,discard 0 1
# /boot was on /dev/sda1 during installation
UUID=b3cae85c-8fc9-4dc9-887b-8b6df563f618 /boot ext2 defaults 0 2
/dev/mapper/cryptswap1 none swap sw 0 0
tmpfs /tmp tmpfs defaults,noatime,noexec,nosuid,mode=1777,size=512M 0 0
#Mount samba shares
//vps/keys /home/kane/keys cifs credentials=/home/kane/.vps-cifs,auto 0 0
#Mount encrypted disks
/dev/mapper/data1 /mnt/data1 ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
/dev/mapper/data2 /mnt/data2 ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
/dev/mapper/parity1 /mnt/parity1 ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
/dev/mapper/parity2 /mnt/parity2 ext4 defaults,errors=remount-ro,x-systemd.requires=network.target 0 2
df -h
Filesystem Size Used Avail Use% Mounted on
udev 7.9G 0 7.9G 0% /dev
tmpfs 1.6G 26M 1.6G 2% /run
/dev/dm-0 94G 42G 48G 47% /
tmpfs 7.9G 12K 7.9G 1% /dev/shm
tmpfs 5.0M 0 5.0M 0% /run/lock
tmpfs 7.9G 0 7.9G 0% /sys/fs/cgroup
tmpfs 512M 24K 512M 1% /tmp
/dev/sdc1 236M 70M 154M 32% /boot
tmpfs 1.6G 0 1.6G 0% /run/user/1000
//vps/keys 8.0G 4.7G 3.4G 59% /home/kane/keys
/dev/mapper/data1 3.6T 2.0T 1.5T 57% /mnt/data1
/dev/mapper/data2 3.6T 2.0T 1.5T 57% /mnt/data2
/dev/mapper/parity1 3.6T 2.0T 1.5T 57% /mnt/parity1
/dev/mapper/parity2 3.6T 2.0T 1.5T 57% /mnt/parity2
I use AUFS to pool all the data disks on both servers and present them to the user as a single share. I use snapraid for redundancy which is what the parity disks are for. The downloads disk is used for storage of dynamic data (as the pool is only for static storage) so it is used for downloads, vms, apt-cacher files, and whatever else I don’t want on the pool or boot disk. The two backup disks are in a btrfs array and are used to backup important data.
I’ve also encrypted swap on both systems.
The scripts
By default the encrypted disks are unlocked automatically on boot as long as the key server is available. So if the servers are removed from the network they can’t unlock the disks. The scripts add additional security by having the servers check that they can still talk to each other and lock the disks and keys if they can’t.
Each system has three scripts:
paranoid-mode, which is a script run every minute by cron. It checks if a lock has been requested and if it has it will run the script to lock the disks. It then checks if paranoid mode is enabled, if not it will exit but if it is it then checks that it can contact the other servers. If it can’t it locks the disks.
a lock script which will lock the disks or keys
and an unlock script which will unlock the disks or keys.
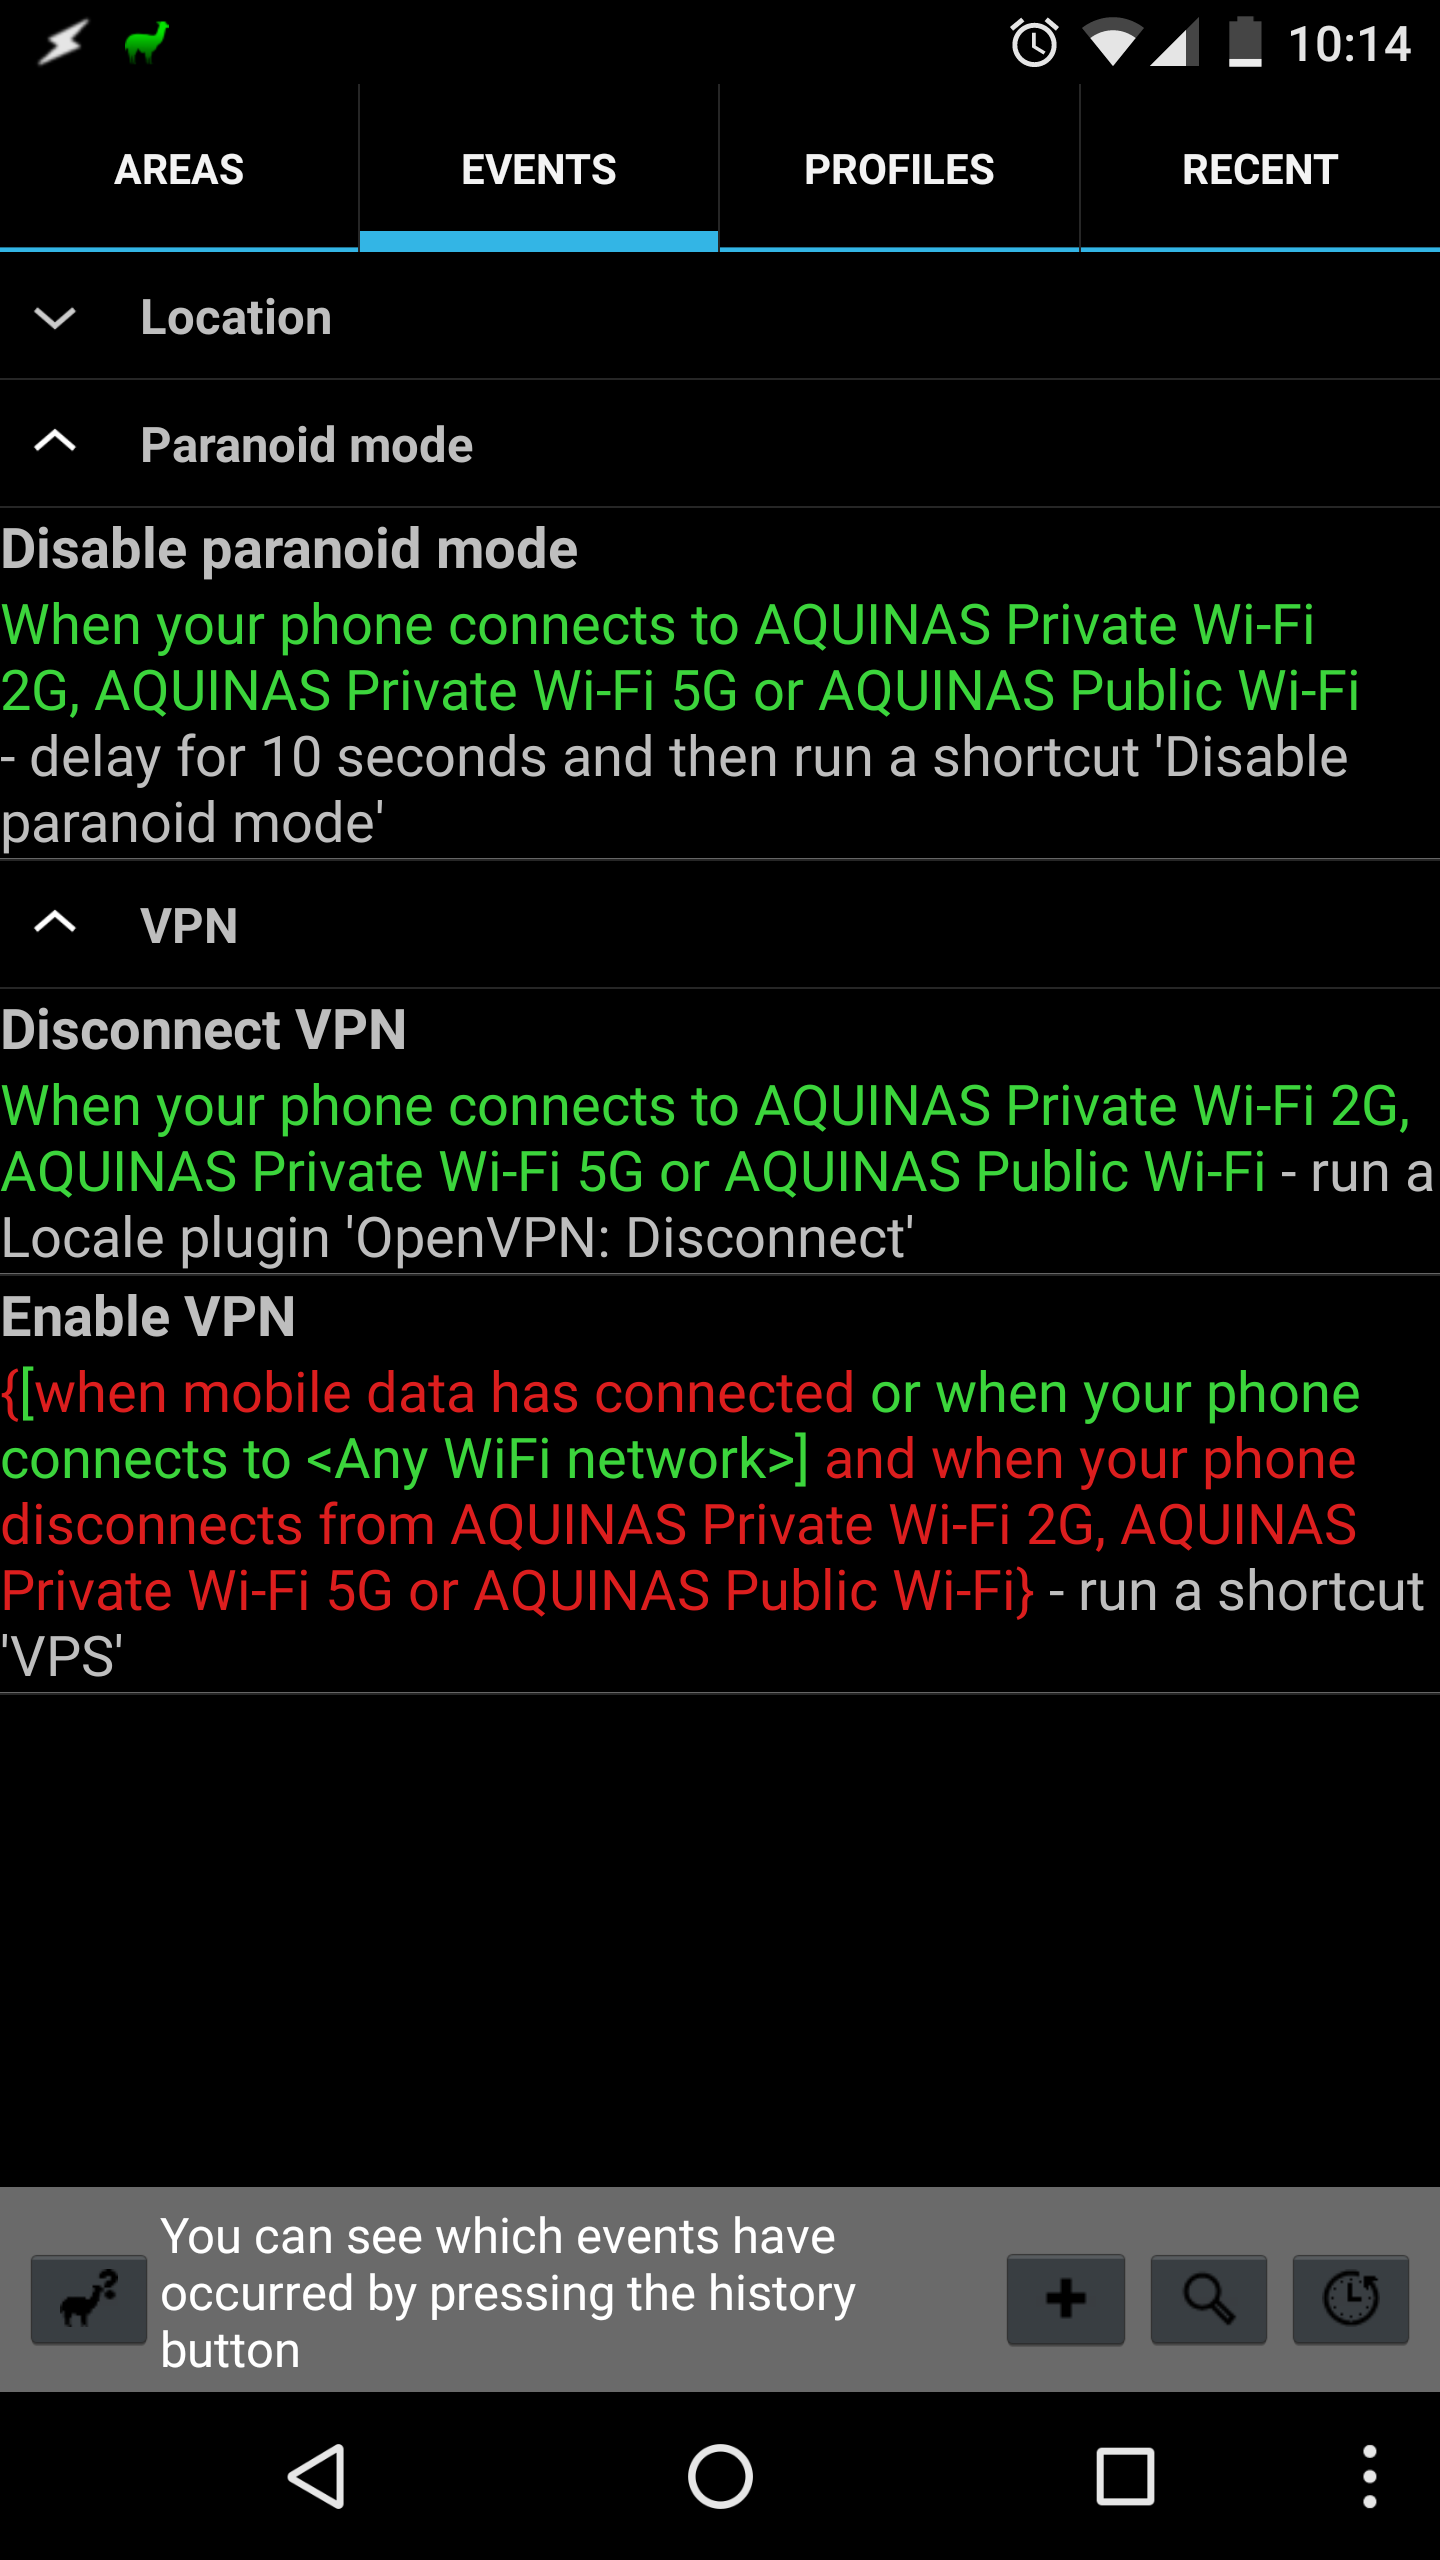
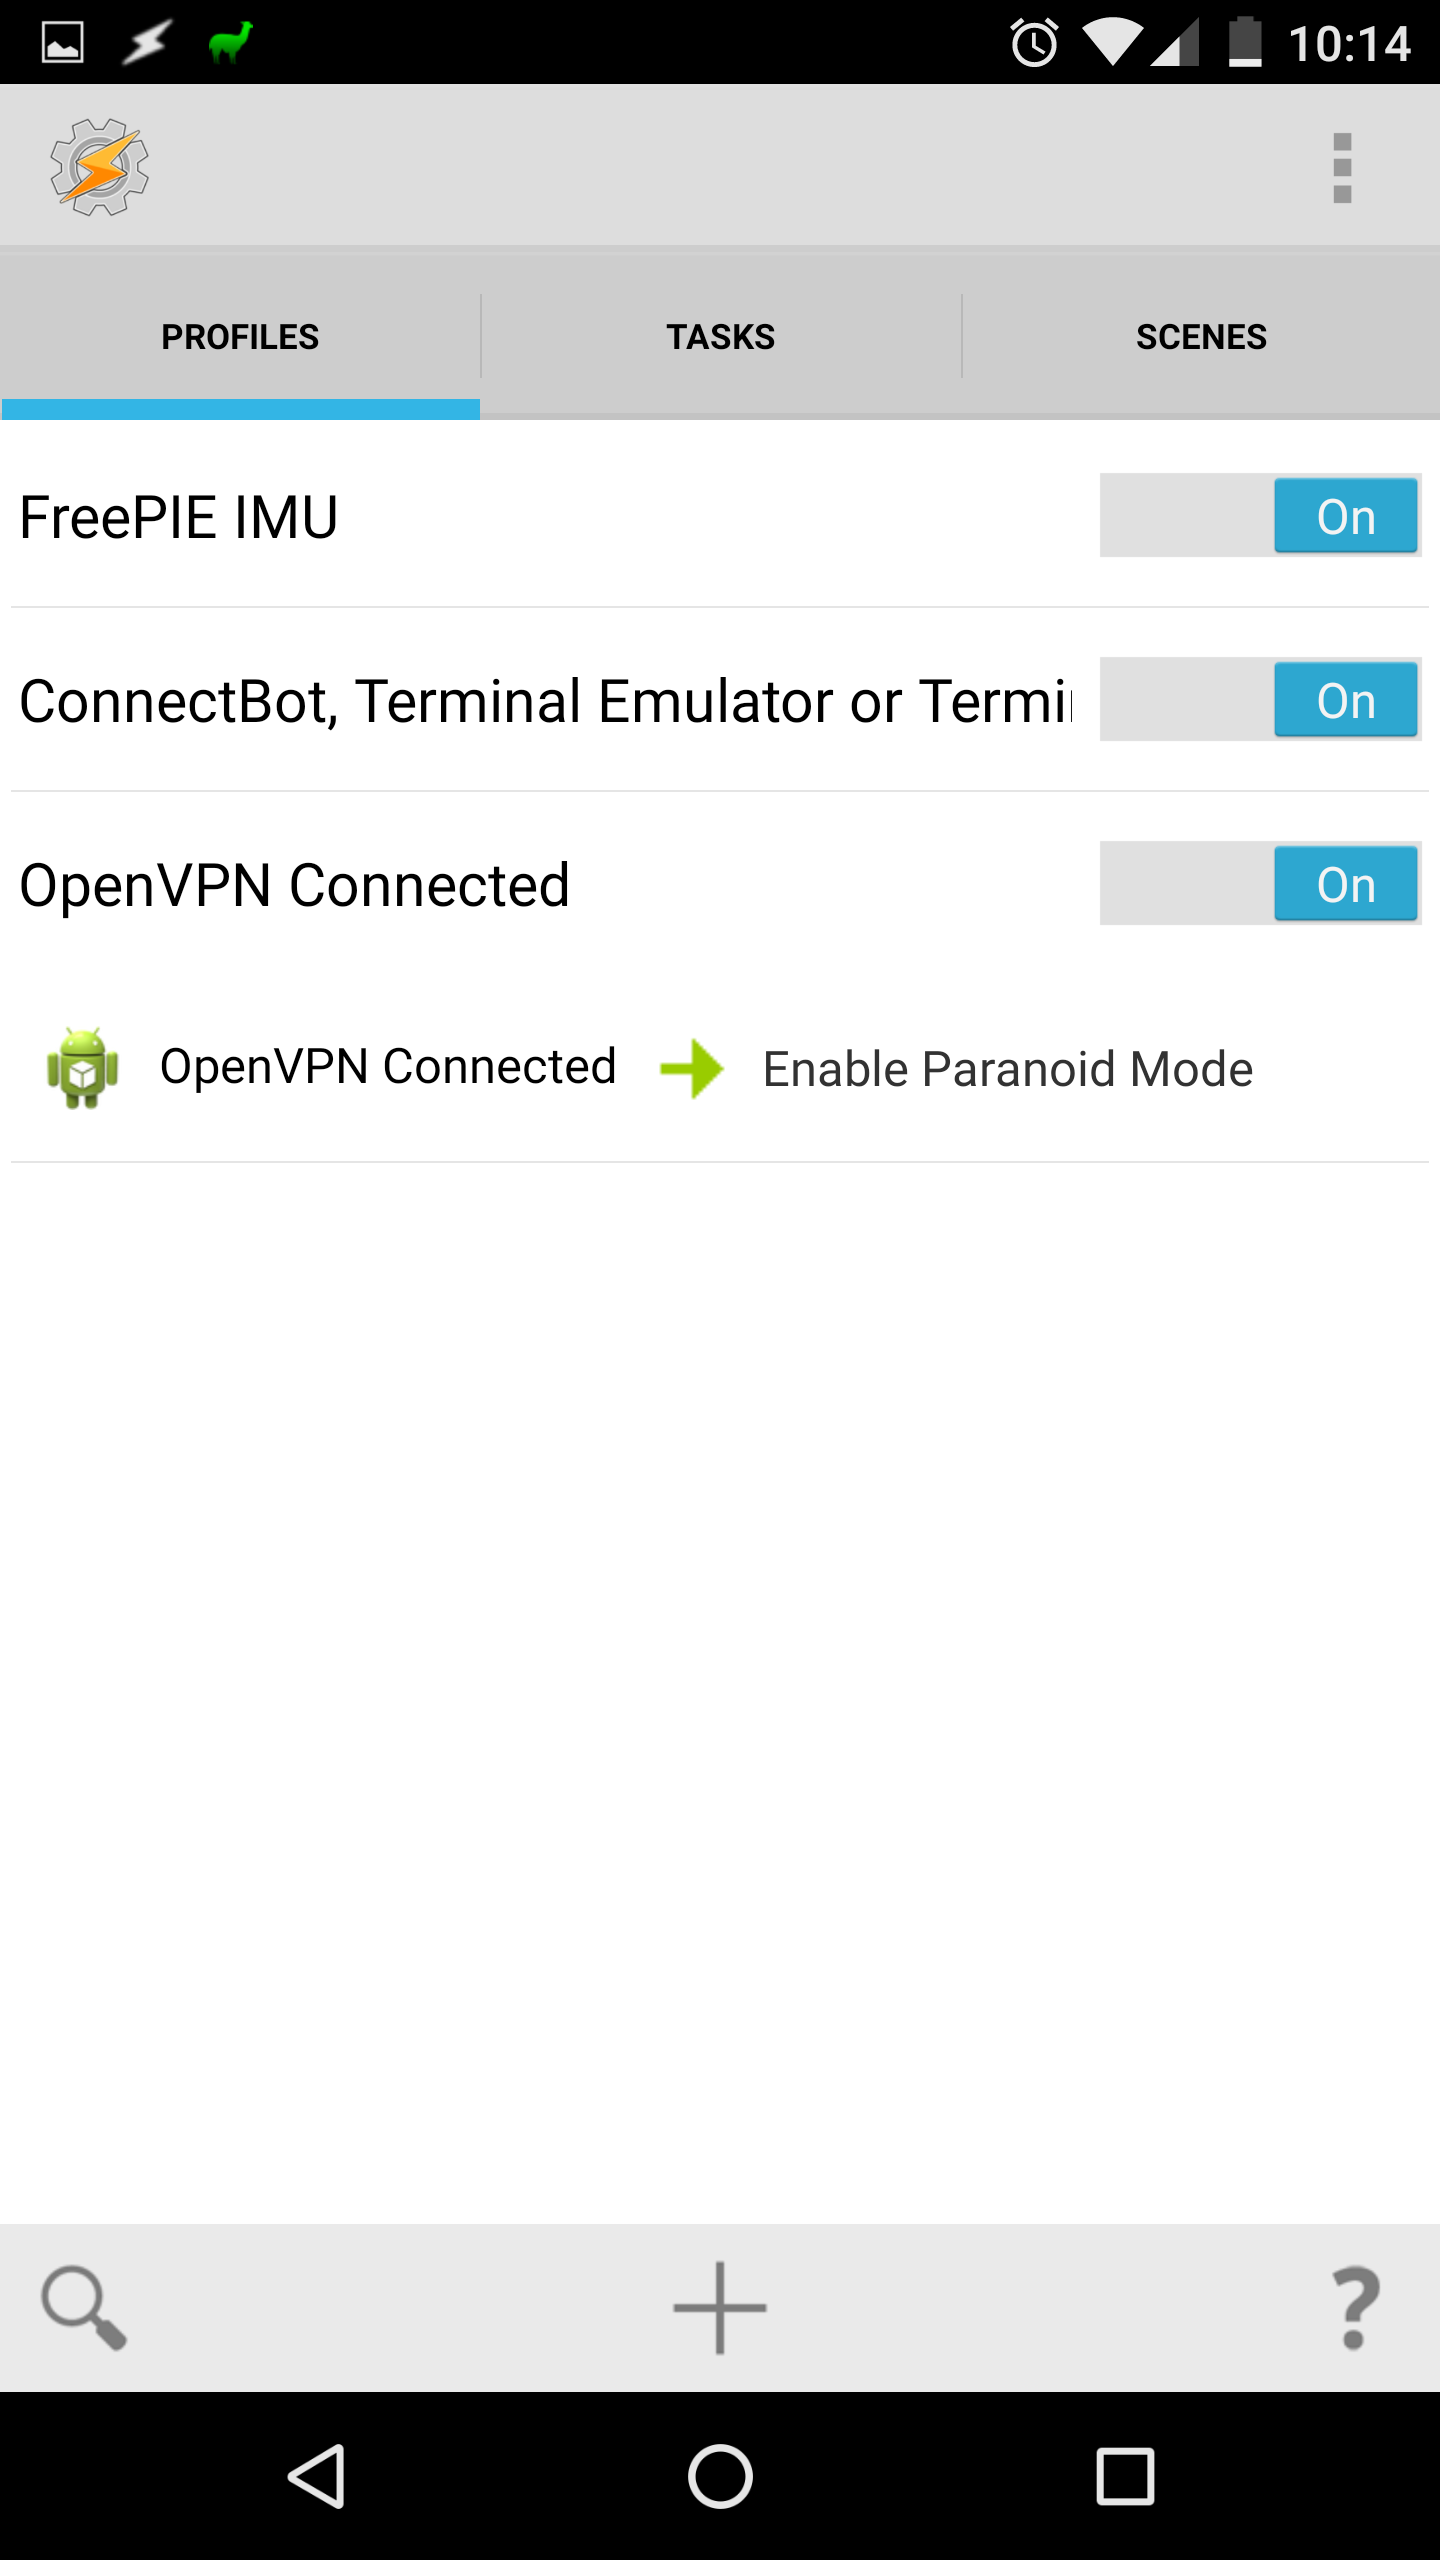
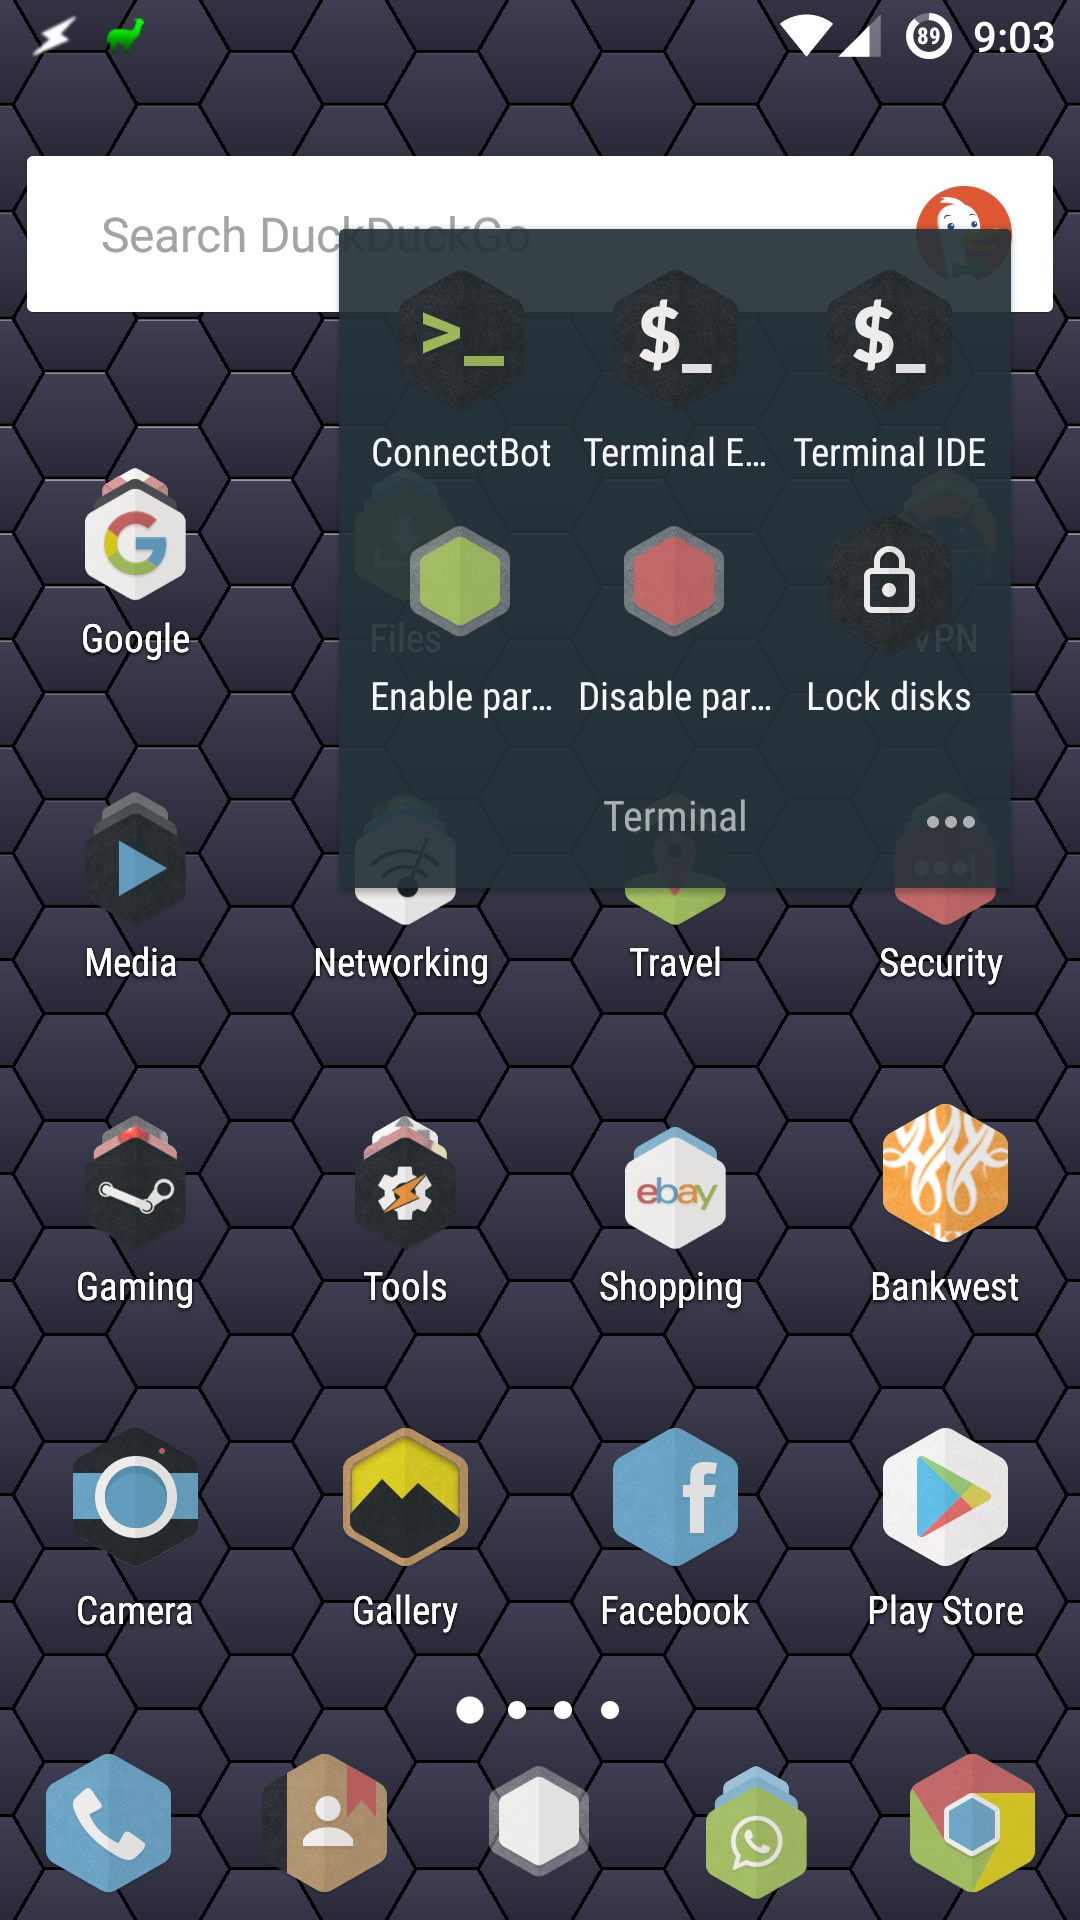
There are also three files whichthe scripts check before running, these are essentially switches which allow me to enable or disable the functions of the script. I’ve set it up this way so that the scripts are run by root via cron but the switches can be set by the regular user. This way I can use shotcuts on my phone to set the different modes.
These files are: .paranoid which sets paranoid mode on or off, .lock which tells the script to lock the disks if it’s set and .locked which tells the script to exit if the disks are already locked.
Additionally there are four more scripts on HELIOS which are used to run scripts and set options on all the servers, these are the scripts which are run by the shorcuts on my phone. They are: enable/disable paranoid mode and lock/unlock disks.
VPS
paranoid-mode.sh
#!/bin/bash
#Check to see if disks are locked
#If disks are locked then exit
LOCKED=$( < /home/administrator/.locked )
if [ $LOCKED -eq 1 ]
then
exit
fi
#Check to see if lock has been requested
#Lock keys if it has
LOCK=$( < /home/administrator/.lock )
if [ $LOCK -eq 1 ]
then
echo "Lock requested, locking keys"
/bin/bash /home/administrator/scripts/lock-keys.sh
exit
fi
#Check to see if paranoid mode is enabled
#If disabled then exit script
PARANOID=$( < /home/administrator/.paranoid )
if [ $PARANOID -eq 0 ]
then
exit
fi
#In paranoid mode keys will be locked if either HELIOS or HYRON are unreachable.
#Check to see if HELIOS is reachable
#Ping HELIOS 10 times but stop after successful ping
((count = 10))
while [[ $count -ne 0 ]]
do
ping -c 1 10.1.1.20
rc=$?
if [[ $rc -eq 0 ]]
then
((count = 1))
fi
((count = count - 1))
done
if [[ $rc -eq 0 ]]
then
HELIOS=1
else
HELIOS=0
echo "HELIOS unreachable"
fi
#if ping -c 1 10.1.1.20 &> /dev/null
#then
# HELIOS=1
#else
# HELIOS=0
# echo "HELIOS unreachable"
#fi
#Check to see if HYRON is reachable
#Ping HYRON 10 times and stop after successful ping
((count = 10))
while [[ $count -ne 0 ]]
do
ping -c 1 10.1.1.22
rc=$?
if [[ $rc -eq 0 ]]
then
((count = 1))
fi
((count = count - 1))
done
if [[ $rc -eq 0 ]]
then
HYRON=1
else
HYRON=0
echo "HYRON unreachable"
fi
#if ping -c 1 10.1.1.22 &> /dev/null
#then
# HYRON=1
#else
# HYRON=0
# echo "HYRON unreachable"
#fi
#If both servers are reachable then exit, else lock the keys
SERVERS=$(($HELIOS + $HYRON))
if [ $SERVERS -eq 2 ]
then
exit
else
echo "Servers unreachable, locking keys"
/bin/bash /home/administrator/scripts/lock-keys.sh
fi
Since the original post I’ve added the lock and locked checks and changed the ping test so that it will check 10 times before deciding that the servers are unreachable. This way the system doesn’t lock just because one packet got lost.
I’m not sure if I’ve changed the lock and unlock scripts other than to incorporate the lock and locked checks. But I’ll post them again anyway.
lock-keys.sh
#!/bin/bash
#Prevent paranoid mode from running lock-keys.sh while keys are locked
echo 1 > /home/administrator/.locked
#Stop samba server
service smbd stop
wait
#Secure erase key files
shred -u /home/administrator/keys/*.key
#Reset lock
echo 0 > /home/administrator/.lock
unlock-keys.sh
#!/bin/bash

#Decrypt key archive
openssl aes-256-cbc -d -a -in /home/administrator/keys/keys.tar.aes -out /home/administrator/keys/keys.tar
wait

#Extract key files from tar
tar -xvf /home/administrator/keys/keys.tar -C /home/administrator/
wait

#secure erase tar file
shred -u /home/administrator/keys/keys.tar
wait

#restart samba server
service smbd restart
#Allow paranoid mode to run lock-keys.sh again
echo 0 > /home/administrator/.locked
HELIOS
Paranoid mode on the NAS servers will check that they keyfiles exist (and are therefore not locked) and that the key server is reachable via ping. This script is virtually identical on both systems.
paranoid-mode.sh
#!/bin/bash

#Check to see if disks are locked
#If disks are locked then exit
LOCKED=$( < /home/kane/.locked )
if [ $LOCKED -eq 1 ]
then
	exit
fi

#Check to see if lock is requested
#If lock is requested then lock the disks
LOCK=$( < /home/kane/.lock )
if [ $LOCK -eq 1 ]
then
	echo "Lock requested, unmounting encrypted volumes"
	/bin/bash /home/kane/scripts/lock-disks.sh
	exit
fi

#Check to see if paranoid mode is enabled
#If disabled then exit script
PARANOID=$( < /home/kane/.paranoid )
if [ $PARANOID -eq 0 ]
then
        exit
fi

#In paranoid mode disks will unmount and close if key files are unreachable
#Check to see if key files exist
if [ -s /home/kane/keys/helios.data1.key ]
then
	KEYS=1
else
	KEYS=0
	echo "Keyfiles inaccessable"
fi
#Check to see if VPS is reachable
#Ping the VPS 10 times, stop after successful ping
((count = 10))
while [[ $count -ne 0 ]]
do
	ping -c 1 10.1.6.1
	rc=$?
	if [[ $rc -eq 0 ]]
	then
		((count = 1))
	fi
	((count = count - 1))
done

#If ping is successful then VPS is up, else VPS is unreachable.
if [[ $rc -eq 0 ]]
then
	VPS=1
else
	VPS=0
	echo "Key server unreachable"
fi

#if ping -c 1 10.1.6.1 &> /dev/null
#then
#	VPS=1
#else
#	VPS=0
#	echo "Key server unreachable"
#fi

#If both keyfiles exist and ping is successful then exit, else lock disks
KEYSERVER=$(($KEYS + $VPS))
if [ $KEYSERVER -eq 2 ]
then
	exit
else
	echo "Key file cannot be accessed, unmounting encrypted disks"
	/bin/bash /home/kane/scripts/lock-disks.sh
fi
lock-disks.sh
#!/bin/bash

#Prevent paranoid-mode from running lock-disks.sh while disks are locked
echo 1 > /home/kane/.locked

echo "unmount key storage"
umount -l /home/kane/keys

echo "Stop samba and apt-cacher"
systemctl stop smbd
systemctl stop apt-cacher-ng

echo "Unmount file systems"
#unmount NFS shares on HYRON so pool can unmount
umount -l /mnt/hyron/data1; wait
umount -l /mnt/hyron/data2; wait
#Unmount pool so data disks can unmount
umount -t aufs -l -a; wait
umount -l /mnt/backups
umount -l /mnt/data1
umount -l /mnt/data2
umount -l /mnt/data3
umount -l /mnt/data4
umount -l /mnt/data5
umount -l /mnt/data6
umount -l /mnt/data7
umount -l /mnt/data8
umount -l /mnt/parity1
umount -l /mnt/parity2

echo "Close Encrypted volumes"
sleep 5
/sbin/cryptsetup luksClose data1
/sbin/cryptsetup luksClose data2
/sbin/cryptsetup luksClose data3
/sbin/cryptsetup luksClose data4
/sbin/cryptsetup luksClose data5
/sbin/cryptsetup luksClose data6
/sbin/cryptsetup luksClose data7
/sbin/cryptsetup luksClose data8
/sbin/cryptsetup luksClose parity1
/sbin/cryptsetup luksClose parity2
/sbin/cryptsetup luksClose backups1
/sbin/cryptsetup luksClose backups2

#Close downloads
echo "Shutdown virtual machines"
virsh shutdown HERA
virsh shutdown CHRONOS
virsh destroy MORPHEUS
virsh shutdown HEPHAESTUS
virsh shutdown HERMES
echo "Waiting 2 minutes for Virtual Machines to shutdown"
sleep 120

echo "Unmount downloads"
umount -l /mnt/Downloads
wait

echo "Close downloads"
sleep 5
/sbin/cryptsetup luksClose downloads


#Reset lock if it was enabled
echo 0 > /home/kane/.lock

echo "Disks locked"
A lot of trial and error went in to getting this script to work properly.
unlock-disks.sh
#!/bin/bash

#Open and mount encrypted disks

#Ensure that keyfile share is mounted
echo "Mount key storage"
mount /home/kane/keys
wait

#If key storage is mounted then unlock disks else report error
KEYS=$( grep -ic "//vps/keys" /etc/mtab )
if [ $KEYS -eq 1 ]
then

	echo "Open encrypted volumes"
	cryptsetup --key-file=/home/kane/keys/helios.downloads.key luksOpen /dev/disk/by-uuid/f319669a-757b-4ad2-a2c3-f83dd8f974ac downloads; wait
	cryptsetup --key-file=/home/kane/keys/helios.data1.key luksOpen /dev/disk/by-uuid/853e9bdf-bf4a-481e-b873-ba6cd39d7011 data1; wait
	cryptsetup --key-file=/home/kane/keys/helios.data2.key luksOpen /dev/disk/by-uuid/4b2250bd-d606-4530-babd-e9494362bfd1 data2; wait
	cryptsetup --key-file=/home/kane/keys/helios.data3.key luksOpen /dev/disk/by-uuid/2811cd52-d9b2-4152-a3af-ee99fd289e23 data3; wait
	cryptsetup --key-file=/home/kane/keys/helios.data4.key luksOpen /dev/disk/by-uuid/69cfb5e5-96c8-449d-b2c8-7ffe852c5525 data4; wait
	cryptsetup --key-file=/home/kane/keys/helios.data5.key luksOpen /dev/disk/by-uuid/52777fbb-553f-46cd-adbb-4c96c9833ec6 data5; wait
	cryptsetup --key-file=/home/kane/keys/helios.data6.key luksOpen /dev/disk/by-uuid/89b5e5e8-4bcf-42f1-becd-1d72ab05edc7 data6; wait
	cryptsetup --key-file=/home/kane/keys/helios.data7.key luksOpen /dev/disk/by-uuid/ae123774-9f7c-49e8-80a1-2d8d4dd2ed9f data7; wait
	cryptsetup --key-file=/home/kane/keys/helios.data8.key luksOpen /dev/disk/by-uuid/f2795c35-f1a8-490e-ad46-45ef23f319d4 data8; wait
	cryptsetup --key-file=/home/kane/keys/helios.parity1.key luksOpen /dev/disk/by-uuid/05e98e23-f0cb-424c-ab12-4527321469e1 parity1; wait
	cryptsetup --key-file=/home/kane/keys/helios.parity2.key luksOpen /dev/disk/by-uuid/bcd3c710-19a9-4054-aa3b-c943a59acc7a parity2; wait

	cryptsetup --key-file=/home/kane/keys/helios.backups1.key luksOpen /dev/disk/by-uuid/209e9133-67fa-4023-8bfa-fc1ce11ac4e3 backups1; wait
	cryptsetup --key-file=/home/kane/keys/helios.backups2.key luksOpen /dev/disk/by-uuid/197ec56d-af4b-4b66-88e3-dcdfa258c4ab backups2; wait

	echo "Mount filesystems"
	sleep 5
	mount -a
	wait

	echo "Start pool and samba server"
	/bin/bash /home/kane/scripts/pool.sh

	echo "Start apt-cacher service"
	service apt-cacher-ng restart

	echo "Start virtual machines"
	virsh start CHRONOS
	virsh start HERA
	virsh start HERMES
	virsh start HEPHAESTUS
	virsh start MORPHEUS

	#Let paranoid mode run lock-disks.sh again
	echo 0 > /home/kane/.locked

	echo "Disks unlocked"

else
	echo "Failed to mount key storage"
	echo "Disks remain locked"
fi
These next scripts are used for the shortcuts
enable-paranoid-mode.sh
#!/bin/bash

#Enable paranoid mode on all servers

#HELIOS
echo 1 > /home/kane/.paranoid

#HYRON
ssh kane@hyron "echo 1 > /home/kane/.paranoid"

#VPS
ssh administrator@vps "echo 1 > /home/administrator/.paranoid"
disable-paranoid-mode.sh
#!/bin/bash

#Disable paranoid mode on all servers

#HELIOS
echo 0 > /home/kane/.paranoid

#HYRON
ssh kane@hyron "echo 0 > /home/kane/.paranoid"

#VPS
ssh administrator@vps "echo 0 > /home/administrator/.paranoid"
request-lock.sh
#!/bin/bash

#Request disk lock on all servers

#HELIOS
echo 1 > /home/kane/.lock

#HYRON
ssh kane@hyron "echo 1 > /home/kane/.lock"

#VPS
ssh administrator@vps "echo 1 > /home/administrator/.lock"
unlock-all.sh
#!/bin/bash

#Unlock all encrypted volumes on all servers
#This needs to happen in order, starting with the key server

ssh -t administrator@vps "sudo /home/administrator/scripts/unlock-keys.sh"
wait

#Next is HYRON, HELIOS must start last in order to correctly mount the pool
ssh -t kane@hyron "sudo /home/kane/scripts/unlock-disks.sh"
wait

sudo /home/kane/scripts/unlock-disks.sh
unlock-all.sh isn’t run by a shortcut, as it requires the input of the sudo passwords on each server aswell as the passphrase to unlock the keys. But I can still run this on my phone using SSH.
For the shortcuts I used an app called handySSH which lets you configure home screen shortcuts with SSH commands.
HYRON
HYRON’s scripts are pretty similar to HELIOS but are a little simpler because there aren’t as many things depending on the disks.
paranoid-mode.sh
#!/bin/bash

#Check to see if disks are locked
#If disks are locked then exit
LOCKED=$( < /home/kane/.locked )
if [ $LOCKED -eq 1 ]
then
	exit
fi

#Check to see if lock is requested
#If lock is requested then lock the disks
LOCK=$( < /home/kane/.lock )
if [ $LOCK -eq 1 ]
then
	echo "Lock requested, unmounting encrypted volumes"
	/bin/bash /home/kane/scripts/lock-disks.sh
	exit
fi

#Check to see if paranoid mode is enabled
#If disabled then exit script
PARANOID=$( < /home/kane/.paranoid )
if [ $PARANOID -eq 0 ]
then
        exit
fi

#In paranoid mode disks will unmount and close if key files are unreachable
#Check to see if key files exist
if [ -s /home/kane/keys/hyron.data1.key ]
then
	KEYS=1
else
	KEYS=0
	echo "Keyfiles inaccessable"
fi
#Check to see if VPS is reachable

#if ping -c 1 10.1.6.1 &> /dev/null
#then
#	VPS=1
#else
#	VPS=0
#	echo "Key server unreachable"
#fi

#Ping the VPS 10 times, stop after successful ping
((count = 10))
while [[ $count -ne 0 ]]
do
        ping -c 1 10.1.6.1
        rc=$?
        if [[ $rc -eq 0 ]]
        then
                ((count = 1))
        fi
        ((count = count - 1))
done

#If ping is successful then VPS is up, else VPS is unreachable.
if [[ $rc -eq 0 ]]
then
        VPS=1
else
        VPS=0
        echo "Key server unreachable"
fi

#If both keyfiles exist and ping is successful then exit, else lock disks
KEYSERVER=$(($KEYS + $VPS))
if [ $KEYSERVER -eq 2 ]
then
	exit
else
	echo "Key file cannot be accessed, unmounting encrypted disks"
	/bin/bash /home/kane/scripts/lock-disks.sh
fi
lock-disks.sh
#!/bin/bash

#Unmount and lock encrypted disks

#Prevent paranoid-mode script from running lock-disks.sh while disks are locked
echo 1 > /home/kane/.locked

echo "unmount key storage"
umount -l /home/kane/keys

echo "Stop samba and NFS service"
systemctl stop smbd
systemctl stop nfs-kernel-server
wait

echo "Unmount file systems"
umount -l /mnt/data1
umount -l /mnt/data2
umount -l /mnt/parity1
umount -l /mnt/parity2

#Restart NFS so HELIOS can lock
systemctl restart nfs-kernel-server

echo "Close Encrypted volumes"
sleep 5
/sbin/cryptsetup luksClose data1
/sbin/cryptsetup luksClose data2
/sbin/cryptsetup luksClose parity1
/sbin/cryptsetup luksClose parity2

#Reset lock if it was enabled
echo 0 > /home/kane/.lock

echo "Disks locked"
unlock-disks.sh
#!/bin/bash

#Open and mount encrypted disks

#Ensure that keyfile share is mounted
echo "Mount key storage"
mount /home/kane/keys
wait

#If key storage is mounted then unlock disks else report error
KEYS=$( grep -ic "//vps/keys" /etc/mtab )
if [ $KEYS -eq 1 ]
then

	echo "Open encrypted volumes"
	cryptsetup --key-file=/home/kane/keys/hyron.data1.key luksOpen /dev/disk/by-uuid/35fc9cd0-0d43-4df0-949e-c545cee47000 data1; wait
	cryptsetup --key-file=/home/kane/keys/hyron.data2.key luksOpen /dev/disk/by-uuid/73f62539-a829-4166-8267-644c095ef27f data2; wait
	cryptsetup --key-file=/home/kane/keys/hyron.parity1.key luksOpen /dev/disk/by-uuid/21295307-169a-4395-aa3e-821e017c5c22 parity1; wait
	cryptsetup --key-file=/home/kane/keys/hyron.parity2.key luksOpen /dev/disk/by-uuid/f1e50579-212a-4774-9ba1-159b87f8e4b0 parity2; wait

	echo "Mount filesystems"
	mount -a
	wait

	echo "Start samba and NFS services"
	systemctl restart smbd
	systemctl restart nfs-kernel-server

	#Let paranoid-mode run the lock-disks.sh script again
	echo 0 > /home/kane/.locked

	echo "Disks unlocked"

else
	echo "Failed to mount key storage"
	echo "Disks remain locked"
fi
So that’s a whole lot of stuff. I probably won’t use paranoid mode much but I thought it would be a fun thing to try and configure. It seems to work alright but I’m sure there would be a more secure and robust way of doing it that would be harder to bypass than just a bunch of bash scripts.
Performance
I don’t think I’ve mentioned this yet but the hardware for the two NAS servers are:
HELIOS: Phenom II X6 1100T
HYRON: Intel Avoton C2750
The performance of the encrypted disks has been surprisingly good. As I discussed in a post bellow using snap raid scrub to check the integrity of all the data after encrypting it ran at a good speed, about 20% slower than normal. scrubbing the data requires reading from all disks simultaneously and verifying checksum data and recalculating parity. So I’m impressed at how well that runs.
As for dingle disk performance I mentioned in that post that I hadn’t noticed any loss in performance and with some basic testing I’ve confirmed that the performance difference is marginal. Bellow I will post benchmark results for each type of disk (I have a mix of disks) as well as a network file transfer.
HELIOS
WD Red 2TB
Raw data read
/dev/sde:
 Timing buffered disk reads: 452 MB in  3.00 seconds = 150.45 MB/sec
Encrypted data read
/dev/mapper/data8:
 Timing buffered disk reads: 428 MB in  3.01 seconds = 142.19 MB/sec
Seagate NAS 2TB (In an external dual bay esata enclosure)
Raw data read
/dev/sdk:
 Timing buffered disk reads: 374 MB in  3.01 seconds = 124.30 MB/sec
encrypted data read
/dev/mapper/backups1:
 Timing buffered disk reads: 326 MB in  3.01 seconds = 108.37 MB/sec
WD Velociraptor 1TB
Raw data read
/dev/sdj:
 Timing buffered disk reads: 584 MB in  3.01 seconds = 194.17 MB/sec
Encrypted data read
/dev/mapper/downloads:
 Timing buffered disk reads: 484 MB in  3.01 seconds = 160.79 MB/sec
HYRON
HGST Deskstar NAS 4TB
Raw data read
/dev/sdd:
 Timing buffered disk reads: 486 MB in  3.00 seconds = 161.84 MB/sec
encrypted data read
/dev/mapper/data2:
 Timing buffered disk reads: 488 MB in  3.00 seconds = 162.55 MB/sec
HELIOS appears to have a small loss in performance, particularly on the external drive and the velociraptor, while HYRON seems to have no loss at all. This is probably due to the phenom II not have AES extensions while the avoton does even though it is a slower processor. Although it could be the IO on HELIOS as it’s a fairly old platform (AM2+ 790X).
In this next test I am copying a game from my desktop to the pool. So it’s going to HELIOS via a samba share, getting sorted by AUFS and sent to HYRON over NFS. (These are steam games which I store in vhd files to make them easy to copy back and forth to the NAS)
So a pretty stable 113MB/s. I’ve seen it get as high at 124MB/s but on average this is the speed I normally get.
Conclusion
Well it took about as long as I expected it to take, ie. a long damn time, but now that it’s complete I’m pretty impressed by the whole thing. Mostly the performance. I was expecting a pretty serious performance hit which has been my experience when using ecryptfs and encfs but with full disk encryption the performance hit is not bad at all. The process to encrypt the disks is simple and most of the complicated stuff that I thought I’d have to figure out in order to auto mount the disks using remote keyfiles was already built in to linux.
My paranoid mode scripts seem to do the job but I will probably continue to tweak them and see what improvements I can make
So now I have ultra paranoid storage to go along with my ultra paranoid network. Now if you’ll excuse me I need to pick up some more tinfoil.