SUCCESSS NTS-NTPSec
Encrypted network time 
On HardenedBSD-OPNsense
@PhaseLockedLoop I have the Protectli Vault 4 Port. Model FW4B-0-8-120. Sorry for delay… wifes needy sometimes and I cant get away much weekends.
A good place to be friend.. a good place to be 
Interesting. Too late to return and get directly from protectli. That would be your easiest route.. but the FW4B should support it. Im not sure why its hanging up
I should go through these at some point and make some changes to my own network. A deep dive into networking in general has been on my list for quite some time. I have all the hardware I’d need, and I’ve already got a decent amount of nginx experience, so I wouldn’t(quite) be starting from scratch just gotta find a spot for it somewhere.
a PITA but its worth it
Seems like everything I need is a pain the ass these days.
Yeah I tried compiling it but its not working when I want to install… so boo
Got sidtracked doing the GPU block for the 3080ti… what a pucker fest…
@PhaseLockedLoop did you use unattended-upgrades package to keep things up todate for your self hosting servers?
Same
I dont use Debian based distros so no. I created my own scripts.
Yeah in that case its sounds like you got a bad or mislabeled unit. Go ahead return. No harm no foul. Order it from the site with coreboot and what you need
Saving a buck isn’t worth it if you get a mislabeled unit. Which happens A TON on amazon
I wrote a salt stack SLS file to automate the pulling of the dnf-automatic packages or yum-cron (my code works for both RHEL 7 & 8) and configures a systemd timer to install security updates automatically for me.
Then about once a month or so I reboot when convenient.
Here is a snippet of my stuff
.
├── pillar
│   ├── common
│   │   ├── packages.sls
│   │   └── repositories.sls
│   └── top.sls
└── states
    ├── automatic-updates
    │   ├── dnf-automatic.sls
    │   ├── files
    │   │   ├── automatic.conf
    │   │   ├── dnf-automatic-install.timer
    │   │   └── yum-cron.conf
    │   ├── init.sls
    │   └── yum-cron.sls
    ├── top.sls
saltstack/states/automatic-updates/dnf-automatic.sls
# For RedHat family, version 8

# Manage the conf file
/etc/dnf/automatic.conf:
  file.managed:
    - source: salt://{{ slspath }}/files/automatic.conf
    - user: root
    - group: root
    - mode: 0644
    - require:
      - pkg: dnf-automatic

# Manage the systemd timer
/usr/lib/systemd/system/dnf-automatic-install.timer:
  file.managed:
    - source: salt://{{ slspath }}/files/dnf-automatic-install.timer
    - user: root
    - group: root
    - mode: 0644
    - require:
      - pkg: dnf-automatic
saltstack/states/automatic-updates/init.sls
{% if grains['os_family'] ==  'RedHat' %}
  {% if grains['osmajorrelease'] == 7 %}
    {% set package_name = 'yum-cron' %}
    {% set service_name = 'yum-cron.service' %}
    {% set state_file = "automatic-updates." + package_name %}
  {% else %}
    {% set package_name = 'dnf-automatic' %}
    {% set service_name = 'dnf-automatic-install.timer' %}
    {% set state_file = "automatic-updates." + package_name %}
  {% endif %}
{% endif %}
include:
    - {{state_file}}

automatic-updates:
  pkg.installed:
    - name: {{package_name}}
  service.running:
    - enable: True
    - name: {{service_name}}
Then in my top state file its included thusly:
  'G@os_family:RedHat':
    - automatic-updates
What this effectively does, is automatically pull packages, configure stuff, and the end result to automatically install just security updates. However, this could be easily configured to install all updates but I wouldn’t something so brash. 
An d if I ever feel like updating it for Debian family I could. Though I only run one Debian sever and that is for my Unifi controller so I am indifferent on that.
DONE and DONE … now if im in gui. atom is loaded and ready to go. If I am stuck without the GUI I have NVIM and the wonderful bloat of ZSH
Thanks for this. When I get more time I’ll look at it. Been very oddly busy this week
Dynamic this is amazing.
Breakage 101
I dont use any debian family products so no hard feelings. Arch and RHEL are the backbone of my infrastructure. With BSD on network devices such as the protectli
This is sweet. I should integrate something like this for Arch. Only security is pushed and then I wait for stable releases of other stuff once a week. Being mostly rolling has been nicer. Ive had fixes for zero days faster
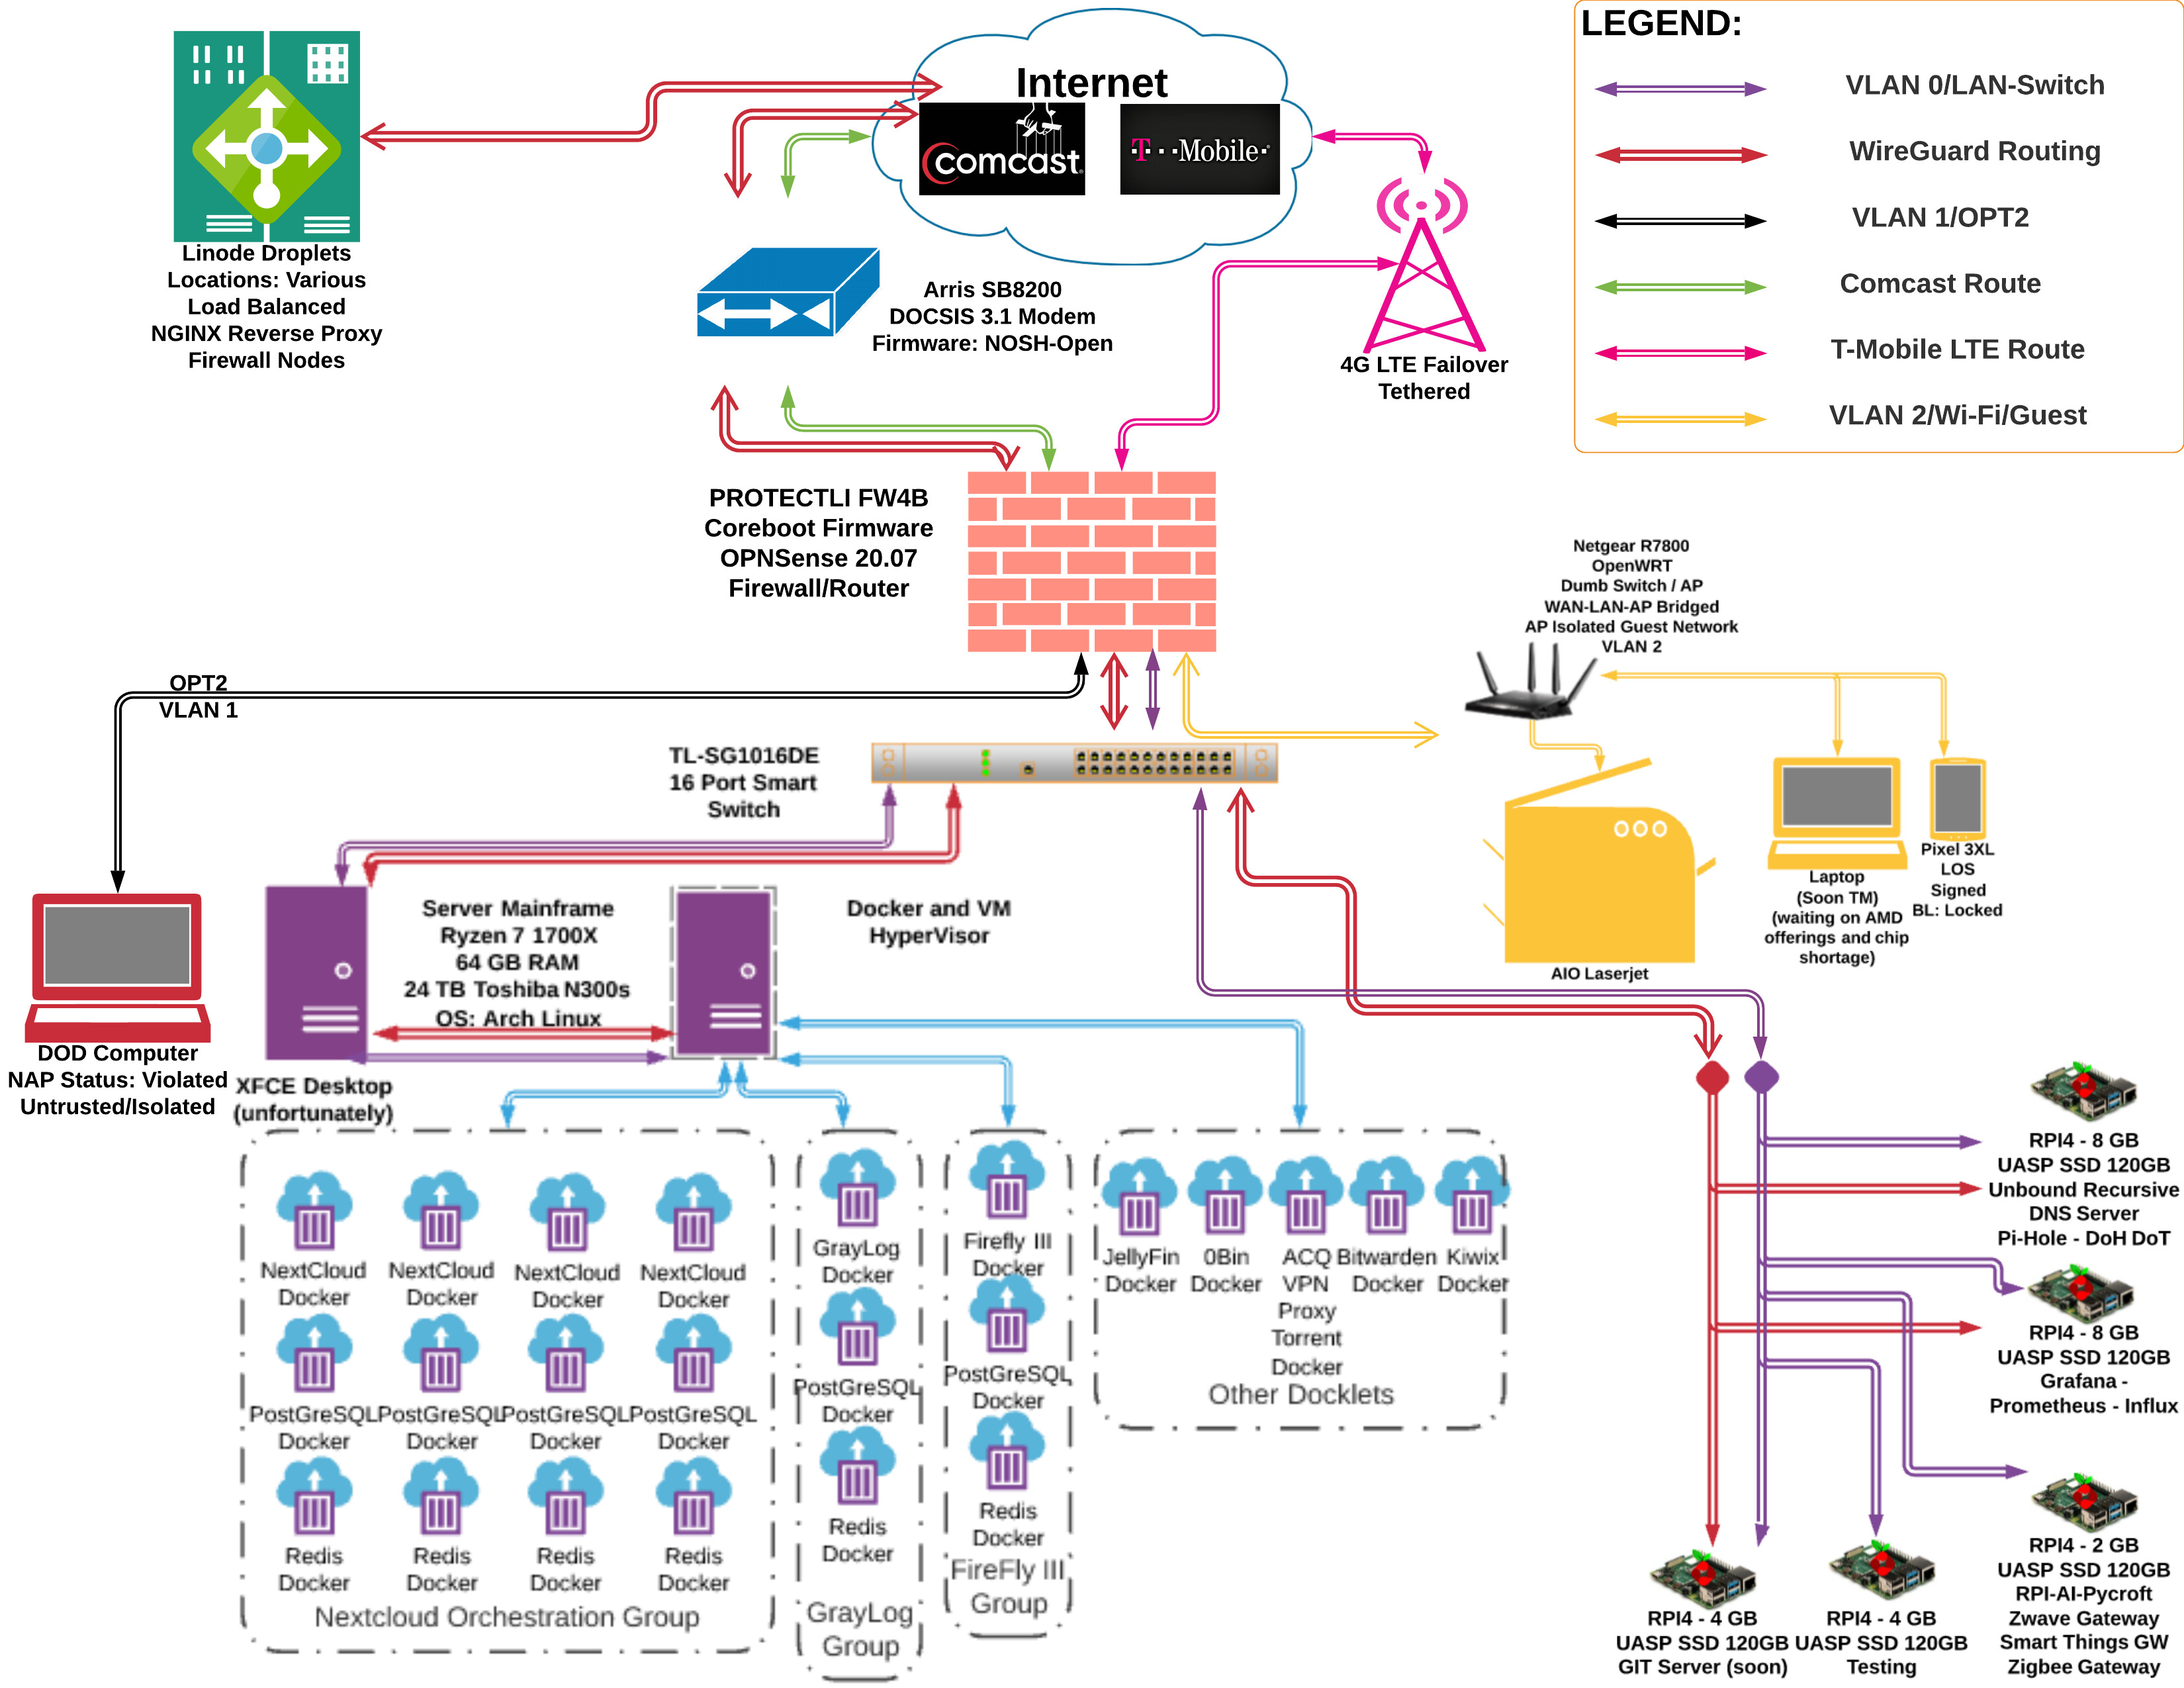
Updated network map
@anon75264233 I’m thinking there are a lot of SPOFs here. What should I try to make redundant?
Ugh I need to get grafana monitoring going… For everything I have. I’m just lazy.
This means
every docker instance
Every NGINX served page
Every NGINX socket proxy
A nice visualization of graylog data
Internal network health monitoring (firewall)
External network monitoring (linode)
Maybe export pihole data to grafana and make it prettier
DoH and DoT termination log visuals…
Etc
Why did I start this. Why do I want nice things. Whiskey is better 
Fantastic net map. I like it.
I made a typo or two
Graylog Group should be Mongo DB and ElasticSearch
Nice diagram. I need to make one myself, did you use the free diagrams.net?
no I used lucid chart and ran out of the free edition
So I cheated and made 6 sectors and lined up the photo/screenshots LOL
I can’t like anything but I would here