Hi guys, I need some help. I have deployed mTLS in OPNsense and want to block access to the web management UIs of my actual services (UPS, APs, etc.), allowing only the public services I created in OPNsense.
Because I have two upstream firewalls, traffic is currently managed by the core switch (Level3) via routing and IP tables. I want to implement another firewall to manage and control the traffic between these services. However, I do not want to deploy a third firewall under the core switch because I don’t have enough 10Gb NICs between the distribution switch and the core switch. I also do not want to convert the core switch to Layer 2 and pass the VLANs up to the Arista NGFW.
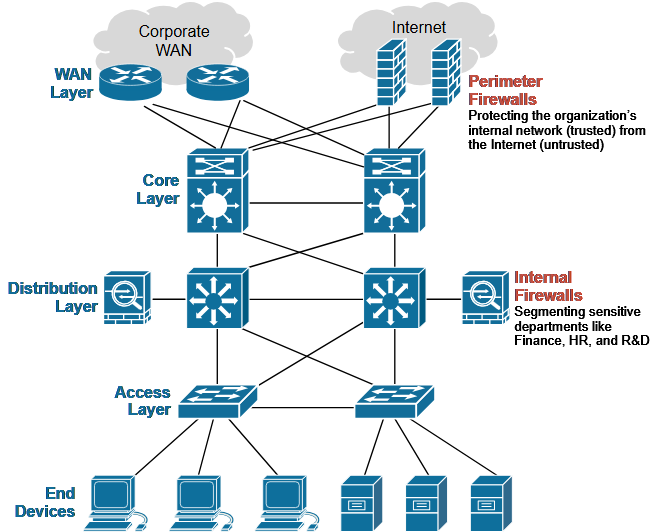
I have seen this specific topology before and want to deploy it, but I am not sure how to engineer a firewall connected to the core switch to handle this traffic segmentation. Any advice?
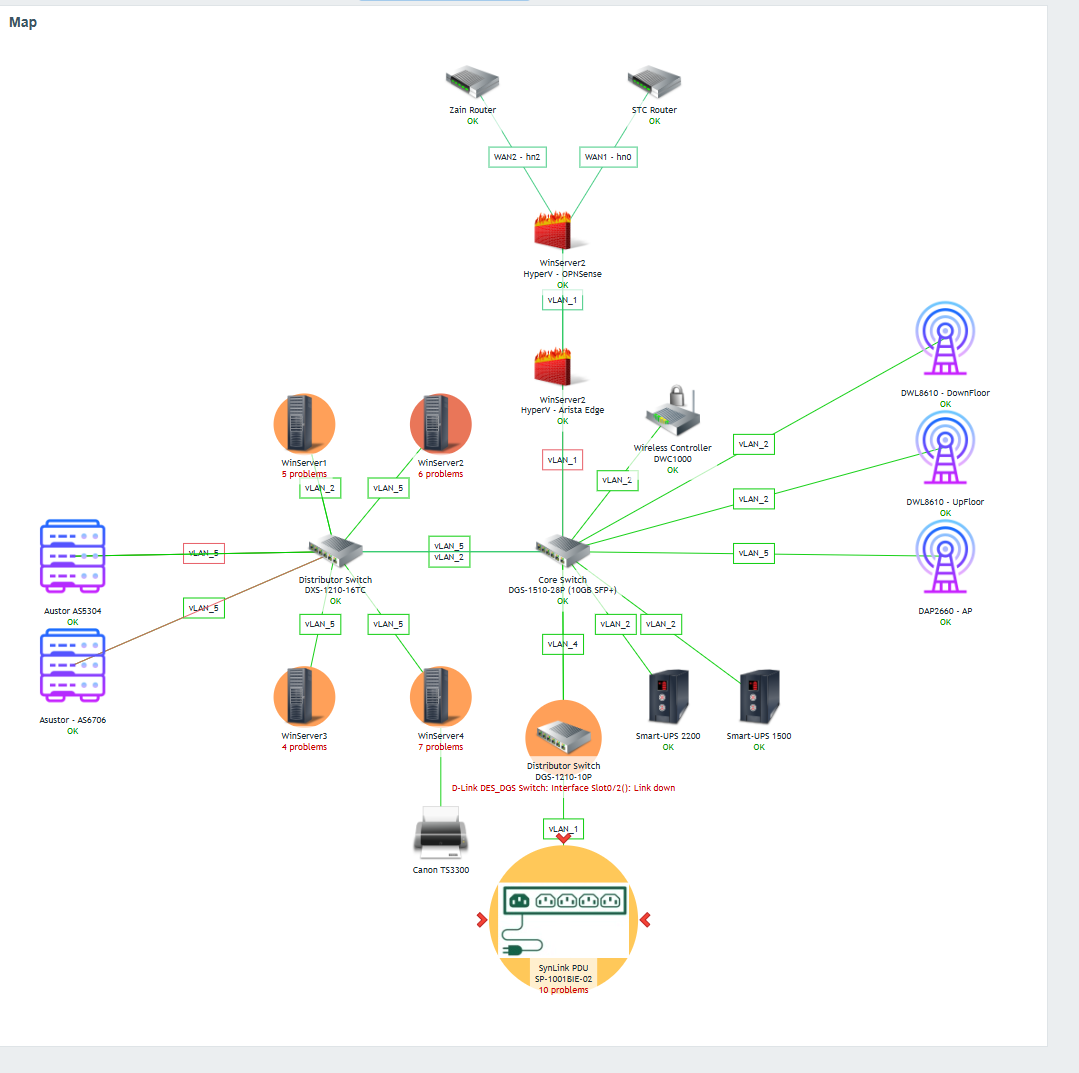
This is my actual setup!
Hey I’m trying to fully understand what you are planning your explanation is not fully clicking.
Migt be on me for not fully being awake.
Do you mind me asking some clarification on 2 parts?
Because I have two upstream firewalls, traffic is currently managed by the core switch (Level3) via routing and IP tables. I want to implement another firewall to manage and control the traffic between these services.
You want to add a 3th firewall to manage traffic between some services.
What are the services you are referring to?
Second
I have seen this specific topology before and want to deploy it, but I am not sure how to engineer a firewall connected to the core switch to handle this traffic segmentation. Any advice?
Are you referring to the top image of the 2? with the example of the hierarchical layers in a high available setup?
Hey, thank you for your reply. My current setup is illustrated in the second picture. I need to block specific types of network protocols (TCP, UDP, etc.), mainly port 443. Since I have deployed mTLS on the OPNsense router located upstream, it does not manage the IP tables. I want to block the web management of the devices located under the core switch.
Oh you might want to set a ACL (acces control list) on it.
Btw mTLS as in all internal trafic is encrypted between hosts and severs?
There is also a old packet layer switching technology with the same mTLS abreviation.
Took me a bit to get it clear for myself.
yes, i have encrypted the web management UI, without SSL you won’t be able to access to the WebGUI… i need a feasible solution to control the real services (e.g. blocking TCP-443) at the local level ..
thank you very much, my switch is cable of performing ACL based on packet contents…
Àh great it was thing you ware looking for.