Abuse of non digital surveillance is a non issue as at the time of those corresponding laws being implemented, it was not viable to log, record and search every conversation made on the network. non digital communication is not ripe for mass abuse. The effort required to abuse these networks is too great to be considered an issue. Once in a while it will be abused, but that’s not at the scale that would be possible with digital surveillance.
Mass surveillance has already proven to be happening with the NSA and it’s suspected that Britain, Australia and New Zealand are doing the same. They do not have the tools to conduct mass surveillance on communications with regards to phone lines and postal services. The amount of work to record every phone call or letter, add to a database and make it searchable is impossibly great. But it’s not with digital services. That’s the difference.
The tools to wiretap phones and look through mail, was given to police with the explicit understanding that it could only be used on a case by case bases due to the difficulty to scaling surveillance. With the internet, that process can and is automated.
We know governments are already abusing data. Giving the government everything by providing a back door in one form or another is arguably a terrible idea. We know they abuse data and you want to give them encrypted, sensitive data?
And all of this doesn’t matter because any kind of back door is a weak point in security, making any form of encrypted data, susceptible to attack from hackers.
The only comment on how this would be implemented is by the Australia government with their bill to try to enforce a client side backdoor (More like a data stream of all data to the government) But as stated after the five eyes conference, these governments have decided that it’s best for the individual governments to decide the best method to approach this. This means that the method our governments want to implement this is up for debate. Which means it’s on topic to discuss different methods of gaining unauthorized access to encrypted data.
That’s like saying that people know crime is bad so they won’t do crime. Just because it goes against the principles of something, doesn’t mean those principles can’t be broken. We are talking about governments wanting to punish organisations for not putting a back door into software of which goes against the principles of encryption in the first place.
Can the process be automated? Yes? then it’s plausible that the government could abuse it with regards to mass surveillance.
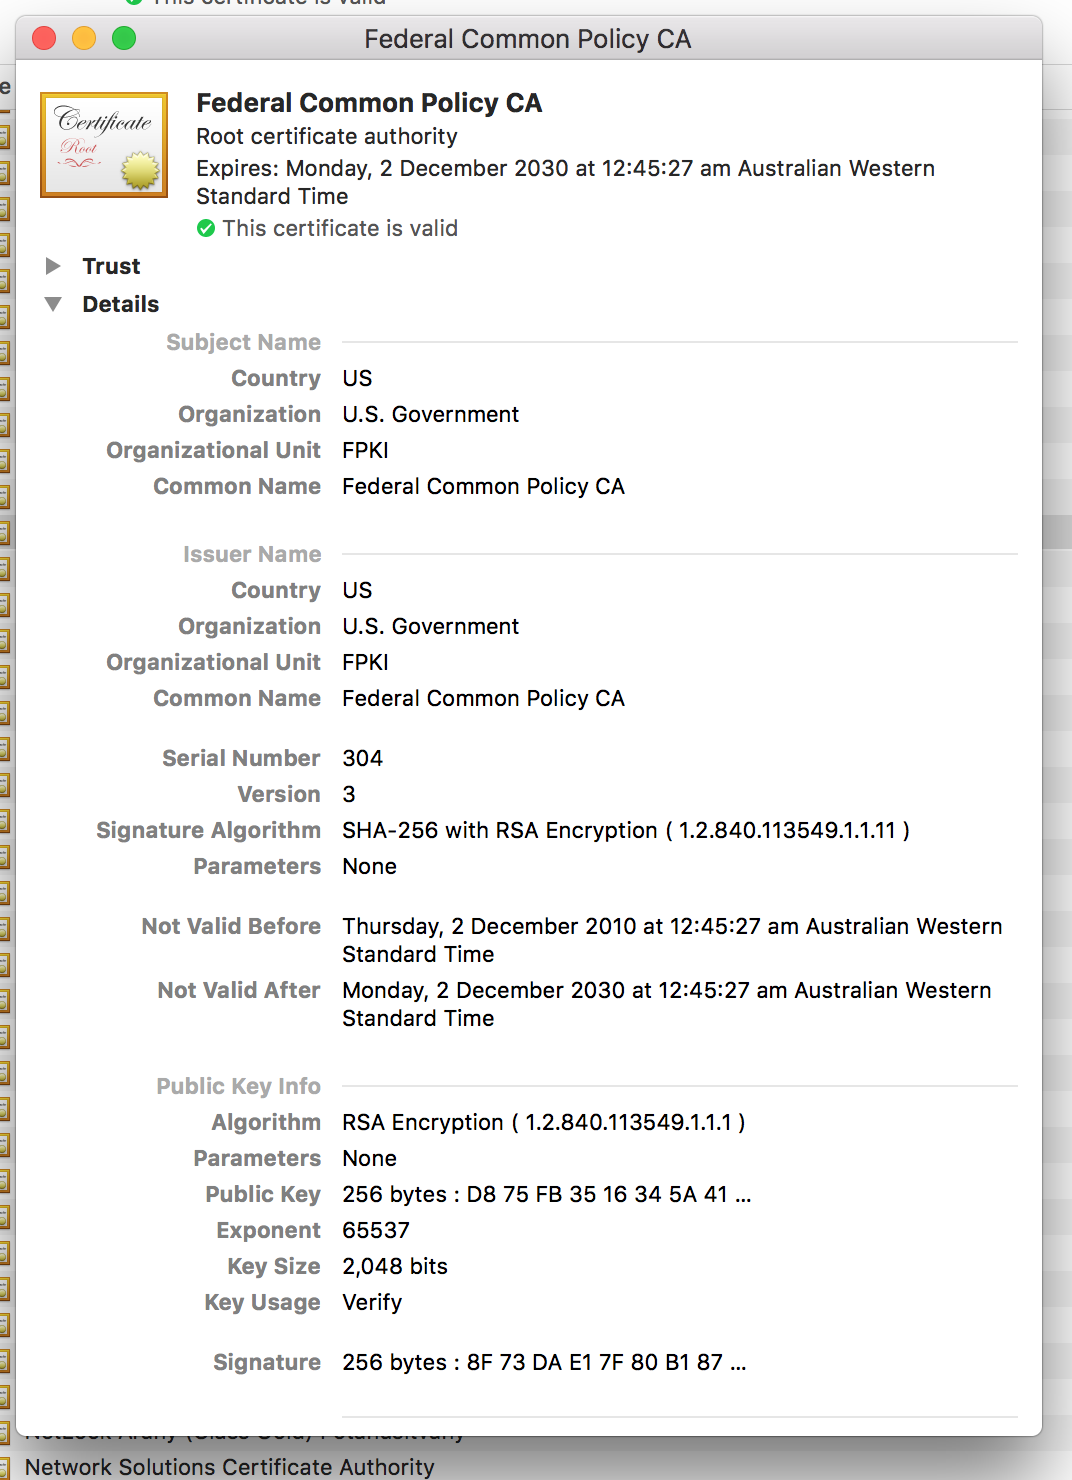
Or invest money into TPM’s that make use of government CA certs. Lobby hardware manufacturers into using it. Or force OS companies to add their CA certs to the OS by default. Might take a bit of time with Linux but Windows and OSX would be big targets.
You’re acting as if you have an abundance of answers but you aren’t disproving arguments mentioned, so far it’s been opinions and an attempt to railroad the conversation in a direction you see fit.