I’m having some issues getting my network to work how I want it to and my brain is now fried and I can’t figure out what I’ve got wrong.
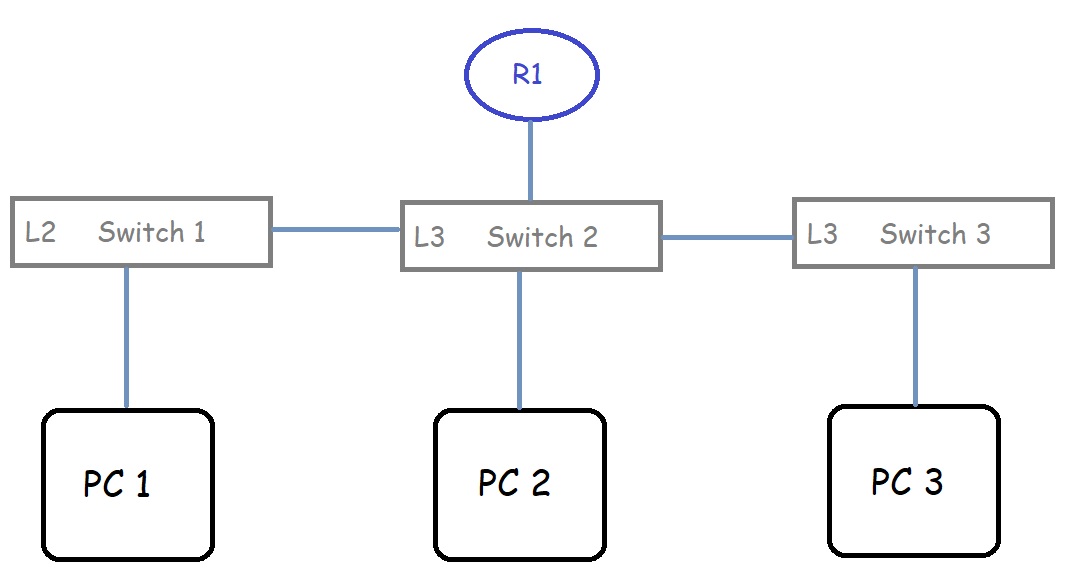
R1 - Internet Router
Has no Vlan capability. Is on Vlan1
IP: 172.16.0.254 (was originally the gateway for the subnet)
No Issue: Can ping PC’s on all Vlans and the internet
Switch 2
This is now configured to do the routing and is the gateway for all subnets
IP:
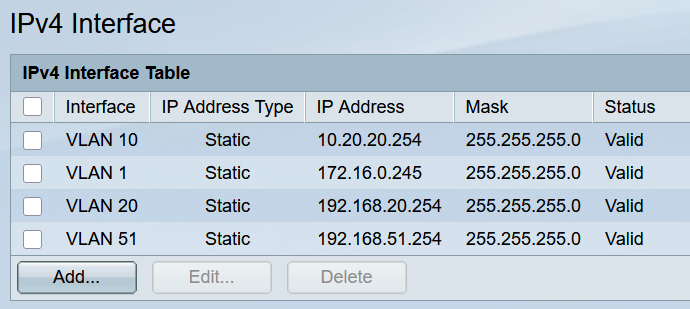
Vlan 1: 172.16.0.245 SM: 255.255.255.0
Vlan10: 10.20.20.254 SM: 255.255.255.0
Vlan20: 192.168.20.254 SM: 255.255.255.0
PC 1
Vlan: 1
IP: 172.16.0.191
SM: 255.255.255.0
GW: 172.16.0.245
No Issue: Can ping PC’s on all Vlans and R1 and the internet
PC 2
Vlan: 20
IP: 192.168.20.201
SM: 255.255.255.0
GW: 192.168.20.254
Issue:Can ping PC’s on all VLans and R1 but not the internet. Trace route to the internet stops at the router
PC 3
Vlan: 10
IP: 10.20.20.201
SM: 255.255.255.0
GW: 10.20.20.254
Issue:Can ping PC’s on all VLans and R1 but not the internet. Trace route to the internet stops at the router
Can anyone suggest to me why PC’s on Vlans 10 and 20 can’t connect to the internet?
It seems to me that the Router is not NAT-ing the 10.0.0.0/8 and the 192.168.20.0/24 networks to the Internet. Since you get a ping through to the other local/private networks, it is routing fine. You verify that with traceroute.
This was the conclusion I was kind of coming to. But I was hoping for concrete confirmation from someone else first.
It wouldn’t surprise me that a cheap home router would work this way. How many home networks have vlans on them with the exception of Guest and IoT wireless vLans.
Is anyone able to confirm they’ve had this issue themselves?
This however leads to me needing to replace my router and then the question comes what with? It seems at this point the best option is likely an old, low power, PC with 2 NIC’s and load it up witha routing O/S.
Imho the issue is in switch 2. The internet router should only see traffic coming from its subnet anyway, either native or natted through switch 2 so it has no idea the other subnets even exist.
Without knowing the switch configuration, i cant say more
I did miss a crucial detail about R1 that is only on one subnet. I assumed that it stands on multiple subnets and you untag the traffic to the router in SW2. @starshipeleven is completely right. Run a traceroute and you will probably see that you have direct connection to the other hosts.
With regards to SW2. It’s routing. Not doing any NAT.
If I do a trace route from PC 1 to PC 3 it hits SW2 and then PC 3. It doesn’t hit the router.
If I do a trace route from PC 1 to the internet. It hits SW2 and then the router and then out to the internet.
If I do a trace route from PC 2 to the internet. It hits SW2 then the router and that’s where it stops.
What do you want to know about the SW2 config? I’ve never known a switch to do NAT between vLans.
Mikrotik uses RouterOS on many of their managed switches and as the name implies its a full router os so it can do whatever (not very fast because the switch CPU is weak).
I assumed other vendors may offer similar features.
Anyway, back to the issue.
If you use intervlan routing the packets keep the original source ip, since there is no NAT.
So if you ping between pcs they know its not an address in same subnet so will ask their gateway, which is switch 2, and it will route correctly. The receiving pc will send its answer to its gateway, again switch 2, and it will route correctly.
If you ping the internet router from outside of its subnet, packet goes to gateway, aka switch 2, then gets routed to the internet router.
At this point the internet router is very confused because its getting a packet with a local ip from a different subnet it knows nothing about. It may or may not try shooting its answer to the ping over its gateway (aka to your ISP, or the internet in general), which is probably rejecting it as local ip range.
Afaik you need to add static routes to the internet router to inform it that to reach stuff from your other subnets it must use switch 2, so it knows where to send its response back.
Will this cheap router have static route settings? Who knows. Lets hope it does
R1 only knows the network 172.16.0., how is R1 supposed to know that when it’s contacted by a pc on 192.168.20. or a pc on 10.20.20. it’s supposed to do some natting? PC1 has a 172.16.0.* address which R1 is familiar with, that’s why PC1 gets nat’ed onto the internet.
So one option is to explain to R1 that it needs to nat for those other networks too, but since it’s an unknown mystery router to the rest of us, I have no idea if it’s capable of that?
Another option is to have SW2 do the natting. Maybe give the SW2 an ip of 172.16.0.200 and have that nat translate all trafic from PC1, PC2 and PC3 into that single address. That way the router sees all traffic comming from the single ip of 172.16.0.200 which R1 is happy to translate into your public ip address on the outside of R1 and everything should work just fine. However since the make and model of SW2 is a mystery to the rest of us, there is no way for me to say whether Sw2 has that capability or not.
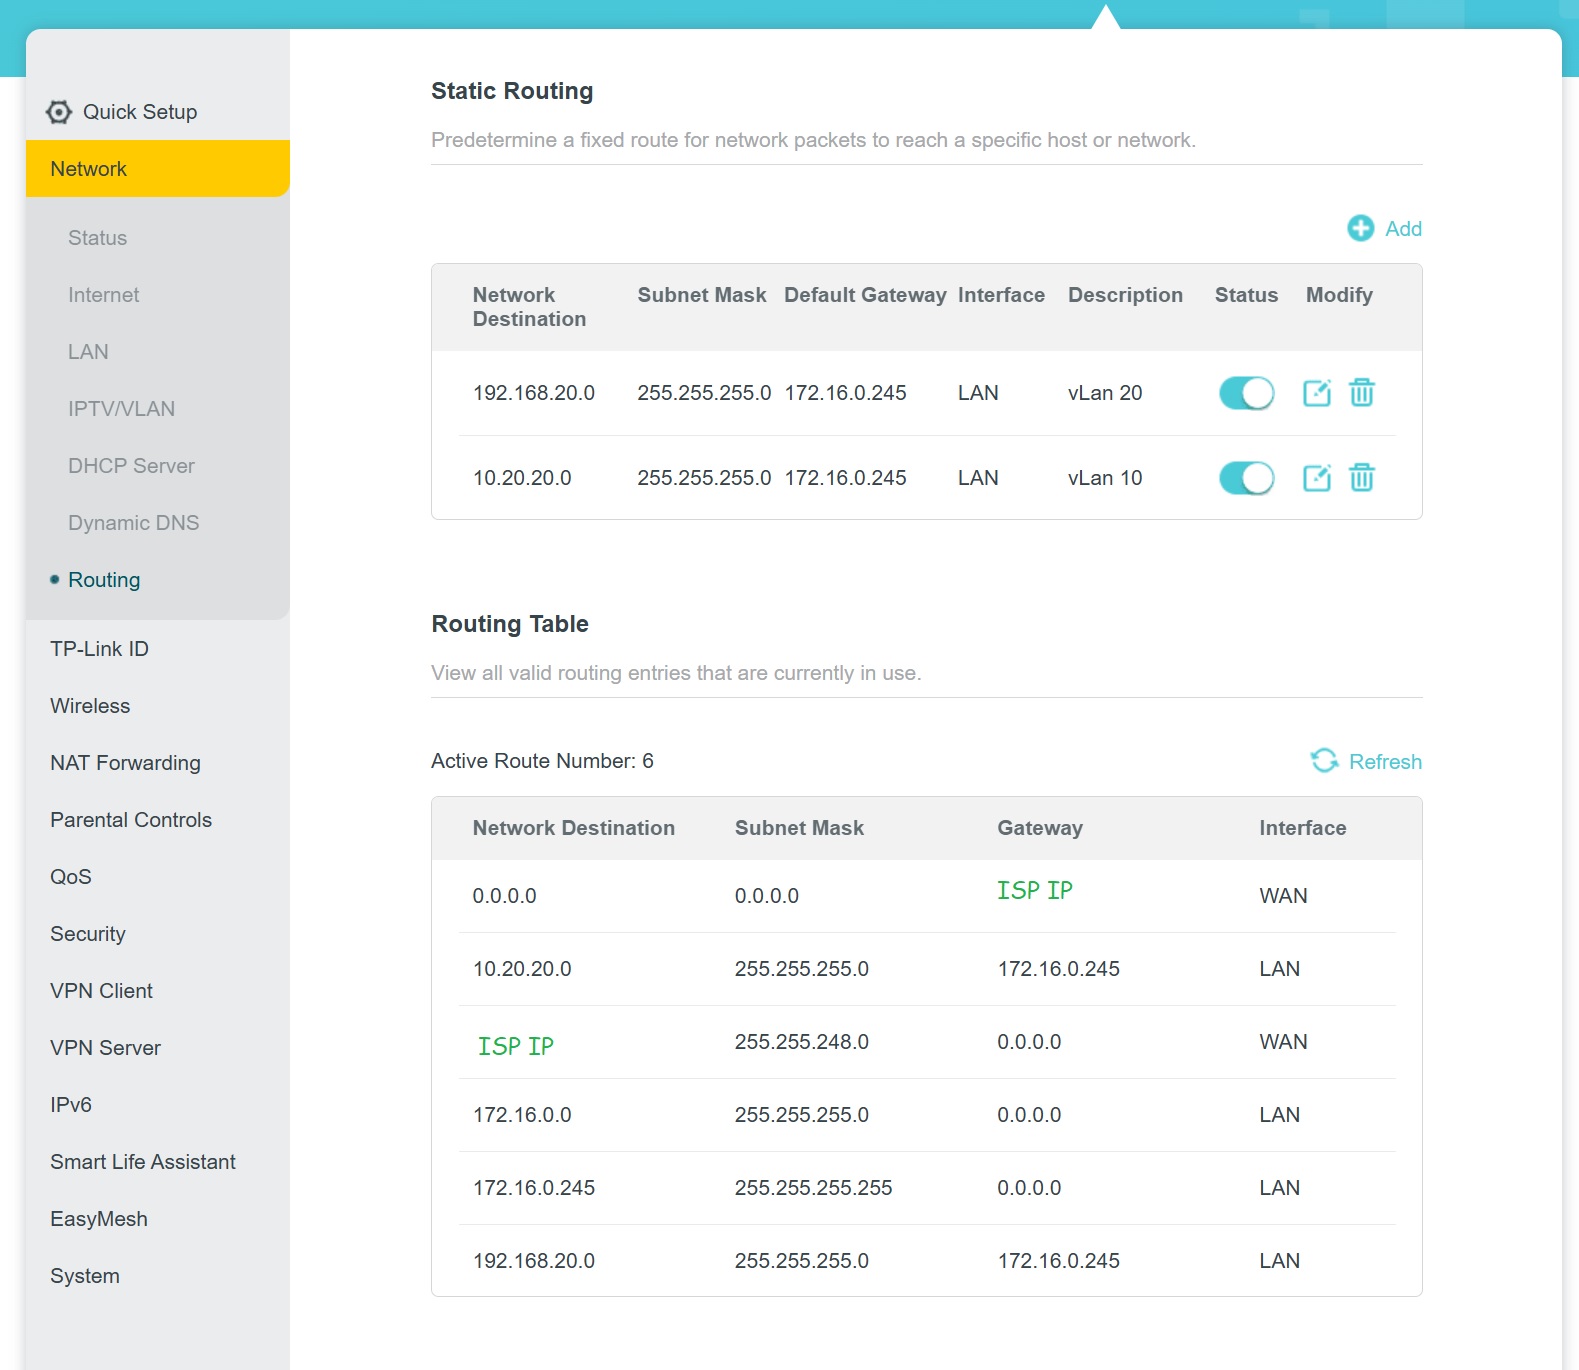
I have indeed put routes on R1 for the subnets in vLan 10 and vLan 20 because that is how it is able to ping PC’’s in all vLans as noted in the OP.
If the router was unable to ping PC’s in vLan10 or vLan20 I’d be less confused as to what is going on.
It appears this cheap router is unable to NAT anything other than devices on its own subnet.
Also as part of testing I’ve create a 2nd subnet on vLan 1 (the default untagged vlan) and created a gateway and route for it and devices on that subnet are also unable to ping to devices on the internet but are able to ping the router and PC’s on all other vLans.
Router is
TP Link AX1800 Wi-Fi 6 Router
Hardware Version: Archer AX1800 v1.20
The only NAT option on it is Enable/Disable.
None of my Switches have NAT options.
At this point I’m prepared to say that the Router is incapable of what is required and thus needs replacing. It’s a cheap $100 Australian router that I bought simply to get me online at the time. It was a temporary solution that has become a little more permanent than liked. At some point my intention is to replace it with something like pf/opnsense that I have more control over. But for now considering this isn’t an obvious quick simple fix of something I’ve overlooked I’m just going to ignore it for the moment.
As far as I can tell the AX1800 is an ethernet to ethernet router, meaning your wan connection is regular ethernet - which makes replacing the router real easy.
Find yourself something like a Dell Wyse 5070 extended with room for an extra network card put some opnsense on it and you have a solid, vlan capable router that uses very little power and is rock solid.
Other good options are Fujitsy s920/s940 just make sure it has the pci-e slot soldered on before buying.
Or if you need a bit more horsepower, a Lenovo m720q and a cheap riser card from ebay.
You don’t need a new router, you need to add static routes on the router back to the 10.20.20.0/24 and 192.168.20.0/24 that point back to the layer 3 router, which is routing between the subnets (172.16.0.245) and/or add a defualt route to the main Layer 3 switch if you don’t already have one.
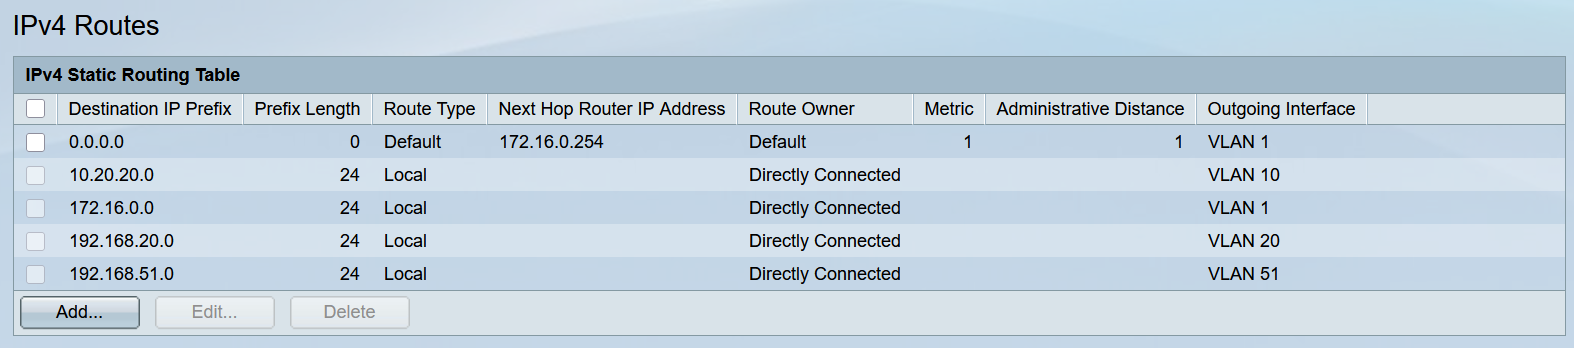
Make sure you have a default route on switch 2 (172.16.0.245) of 0.0.0.0/0 (maybe shown as default route) to 172.16.0.254
I’m also assuming you have routing disabled on switch 3 and you’re using it like a standard layer 2 switch, and that you are using an untagged port on vlan 1 to the router.
I had a quick look how to do this on your particular router:
Log into the router then:
Go to Advanced > Network > Routing.
Click Add
Enter the following:
Network Destination: 10.20.20.0
Subnet Mask: 255.255.255.0
Default Gateway: 172.16.0.245
Interface: LAN
Description: Route to VLAN10
Save
Click Add
Enter the following:
Network Destination: 192.168.20.0
Subnet Mask: 255.255.255.0
Default Gateway: 172.16.0.245
Interface: LAN
Description: Route to VLAN20
Save
EDIT: Forgot to mention you need to set the defualt gateway on the clients to the IP address of that subnet on switch 2, so for clients on vlan1: 172.16.0.245, vlan 10: 10.20.20.[switch 2 address on this subnet], vlan 20: 192.168.0.[switch 2 address on this subnet]
That should be it, I personally would create another vlan on switch 2 (the local router) for clients (lets call it vlan 30 in this case) and then leave the untagged port on vlan 1to the router (and also another port so you can manage vlan1 directly), and then add the other ports for clients on the switch to the new vlan. You will need to add another corresponding reverse route on the router as we did for the 2 networks above.
roiter I appreciate you want to help. But when you help someone ensure that you fully and completely read ALL the information they have provided and make sure you understand it clearly before offereing said help. Otherwise you’re just wasting both their time and your own.
You’re wrong. I’ll give you a chance to redeem yourself by letting you read the OP again and coming back here and telling me what the one line of information is that is within it which says so, else I could lambaste you by pointing it out.
It’s extremely frustrating to have people offer “solutions” that clearly aren’t solutions when information has already been provided from the get go which says your offered solution isn’t actually going to work.
Steady on tiger. To be quite honest ALL of the information required wasn’t provided (the routing table on switch 2 and the router would have gone a long way), so I went from the top. You’re probably going to mention that you could ping all the other PCs from the router, so the reverse routes are in (although I don’t know what subnet mask you have set them to).
Unless your Internet router is totally broken and not routing at all your setup will work (insert here a bit about being a senior network consultant & troubleshooter for over 25 years for major blue chip companies, government organizations and the military as well as being a CCNA, but what would I know). But feel free to ‘lambaste’ me if it makes you feel better.
Did you do all of what I said (pinky promise)? And yes I admit I missed a little bit of what you said, but I did read it all. I should have just asked “Are you sure you have a global route of 0.0.0.0/0 172.16.0.254 on switch 2 (your main subnet router)?”, as lacking that on switch 2 and only having a default route on VLAN1 to 172.16.0.254 (by the way, if you have one of those remove it) would exhibit ALL of the symptoms you mentioned.
Yeah, you nailed it. Without routes on R1 how would it be able to ping PC’s on other local subnets/vlans?
It’s frustrating getting a wall of text telling me how to do stuff I’ve already done, particularly when a conclusion can be drawn from information provided that it has been done (even if not correctly and needs double checking).
However I apologise. I threw you in the same basket as other poor advice I’ve received from new accounts from people who haven’t fully understood the problem. (I’ve had one person tell me I need to set the gateway to 172.16.0.245 for ALL subnets and I’m sure I don’t need to tell you why that won’t work)
However you’ve now suggested one thing which is interesting to me and annoyingly I don’t think I can do anything about.
For reference so you can double check everything I’ve done.
You said I need a Global Route and not a Default Route on SW2.
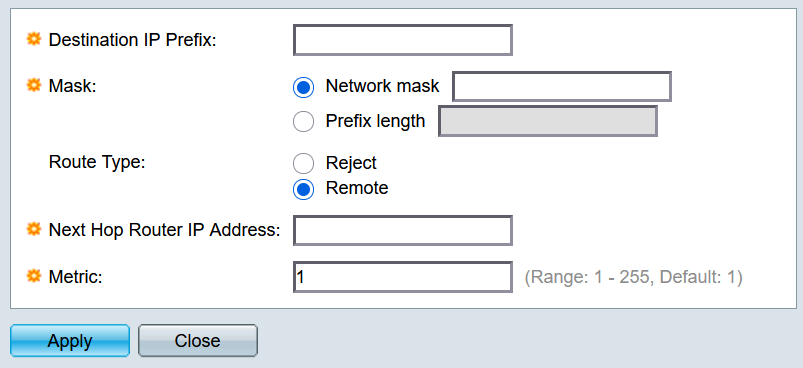
That first route, looks like the Default Route which you speak of which you say I need to get rid of. But what I don’t think I can do is add the Global Route (also I’m not quite sure I understand how it’s different to the Default Route).
For reference, here’s the interface I get when I hit the add button.
No problem btw. Sw2 config looks fine, but why has the router got a routing entry one from bottom of 172.16.0.245/255.255.255.255 that thinks it is the routers lan port address, I thought it was meant to be 172.16.0.254 on the router as.245 is the port on sw2, if it showing . 254 on the router, you might want to reboot that and recheck it.
OK, so here’s an update. I finally got around to doing more testing and made some changes.
R1
IP: 172.16.0.254
SM: 255.255.252.0 (/22)
This now makes my IP space 172.16.0.1 - 172.16.3.254
I created a new vLan, vLan 30.
I configured it’s IP space to be 172.16.1.0/24
This puts it’s IP space inside the IP space configured on the router.
I added a route on the router for 172.16.1.0/24 to point to 172.16.0.245
I added the necessary configuration on SW2
I added a device on IP 172.16.1.3 with SW2 as the gateway on 172.16.1.254 on vLan 30
From that device I’m able to ping all devices on the network and ALSO THE INTERNET.
In theory, this shouldn’t work. In practice it is. WEIRD.
I’m not going to lose any more sleep over this. There’s a big enough IP space there that I don’t care that I can’t use 10.0.0.0 or 192.168.0.0 IP Spaces.
I just figured anyone who ran into the same issue I had with the same router would appreciate this final closure.
I do have the option to expand the IP space further, which I’ll likely do. These were just random ranges chosen for testing purposes.